


Vulnerability: Page
-

Citrix via Flickr
Citrix issues patch for third exploited flaw in NetScaler
The memory overflow vulnerability could lead to a denial-of-service condition under certain circumstances.
By David Jones • Updated Oct. 5, 2026 -
 Courtesy of Fortinet
Fortinet warns that critical flaw in FortiMail is facing exploitation
Security researchers said that attackers can gain access to credentials, stored mail and other connected systems.
By David Jones • Oct. 2, 2026 -
 Explore the Trendline➔
Getty Images
Trendline
Vulnerability Management
The rapid advancement Ai has changed the debate over secure software in the entrprise.
By Cybersecurity Dive staff -
 Justin Sullivan via Getty Images
Mass exploitation of Citrix NetScaler: What we currently know
Suspected state-linked actors targeted critical vulnerabilities in the widely used platform, causing widespread disruption across Europe and North America.
By David Jones • Sept. 30, 2026 -
 Justin Sullivan/Getty Images via Getty Images
Citrix NetScaler exploitation began days before public notification
Customers need to check systems for compromise prior to patching, because the security upgrade may not fully resolve an infected system.
By David Jones • Updated Sept. 29, 2026 -
 Getty Images
Kiteworks lifts advisory after precautionary warning for customers to shut down systems
The firm had received information from law enforcement of a possible attack.
By David Jones • Sept. 28, 2026 -
Citrix via Flickr
Citrix urges immediate upgrades of NetScaler amid widespread exploitation attempts
Security teams received urgent calls to disconnect servers before authorities confirmed critical zero-day flaws.
By David Jones • Sept. 28, 2026 -
 Asanka Ratnayake via Getty Images
Niche AI tools pose major cybersecurity risk to infrastructure operators
Security vetting tools and processes weren’t designed with obscure AI services in mind, according to TrendAI.
By Eric Geller • Sept. 28, 2026 -
 Courtesy of Wiz
Wiz uses AI to find vulnerabilities in critical infrastructure
The Google subsidiary, which helped a railroad and two hospitals, invited others to apply for its free scanning service.
By Eric Geller • Sept. 24, 2026 -
 Getty Images
Insurance sector begins to offer clarity on AI-related cyber claims
The emergence of agentic AI and frontier models has led to widespread uncertainty for policyholders.
By David Jones • Sept. 22, 2026 -
 Getty Images
China-nexus actor steals thousands of documents in monthslong exploitation campaign
Researchers suspect the hacker employed LLMs to develop custom tools.
By David Jones • Sept. 21, 2026 -
 Permission granted by Arctic Wolf
Sponsored by Arctic Wolf
More CVEs than ever. The same old ones keep getting exploited.
Vulnerability volume is climbing fast. The exploited ones are old and already patchable.
Sept. 21, 2026 -
 Getty Images
CISA ends weekly vulnerability roundups as part of shift to prioritization approach
The agency wants to help companies sort through the AI-fueled avalanche of bug reports.
By Eric Geller • Sept. 18, 2026 -
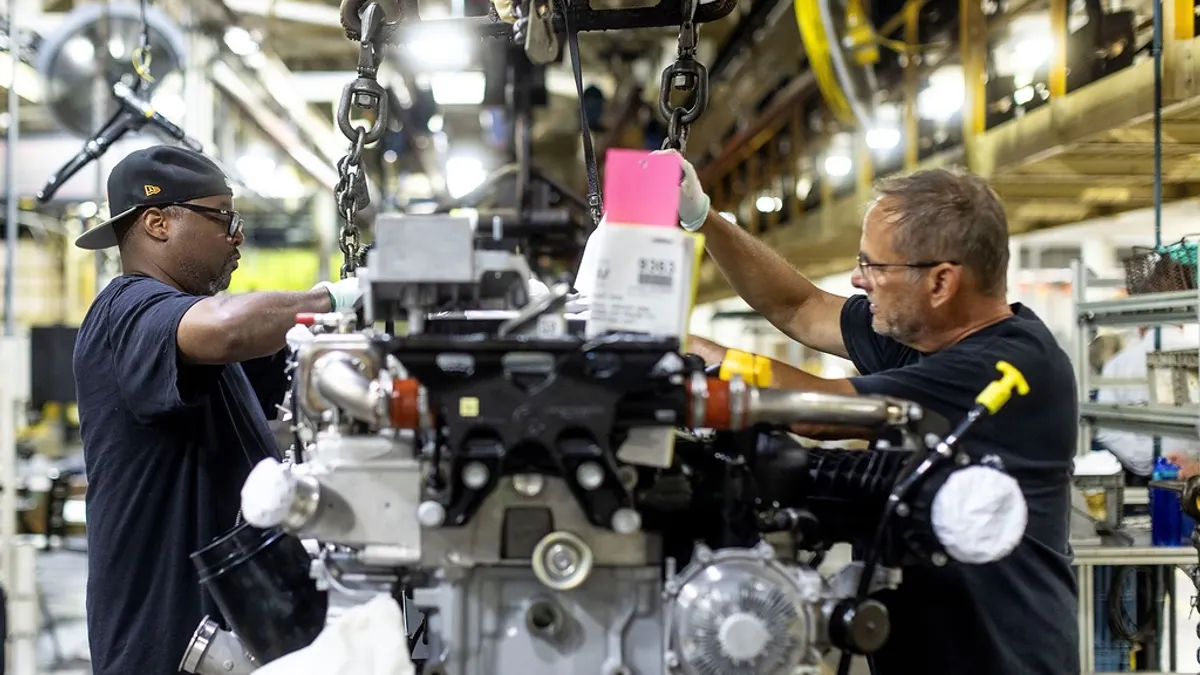
Retrived from Daimler Truck
Manufacturers make patching progress, but identity management still major weakness
Misconfigurations remain widespread in the manufacturing sector, including internet-accessible remote-access software, a new report found.
By Eric Geller • Sept. 17, 2026 -
 David Ramos via Getty Images
Hackers exploit zero-day flaw in Cisco email gateway
Researchers warn the vulnerability could be used by state-linked actors for espionage.
By David Jones • Sept. 16, 2026 -
 Getty Images
Security teams increasingly outflanked by AI agents
A report warns that non-human identities are growing beyond the ability of existing systems to track.
By David Jones • Sept. 14, 2026 -
 tadamichi via Getty Images
Malicious actors already using critical GitLab flaw, CISA and others warn
The vulnerability could let unauthenticated users access sensitive files from software-development environments.
By Eric Geller • Sept. 14, 2026 -
 Getty Images
N-able issues patch for zero-day flaw
Security researchers warned the company of unusual threat activity in a recently patched N-able environment.
By David Jones • Sept. 8, 2026 -
 Permission granted by SonicWall
SonicWall urges immediate patching of chained vulnerabilities
Just weeks after a wave of ransomware attacks, new flaws in SMA1000 series appliances are being exploited.
By David Jones • Sept. 3, 2026 -
 Courtesy of Office of the Texas Governor
Frontier AI helps exploit flaws in tests using key industrial devices
A report showed that Claude could help hackers develop attack strategies targeting PLCs used by water utilities and other industries.
By David Jones • Sept. 1, 2026 -
 Getty Images
PaperCut issues emergency patches as threat actors target chained vulnerabilities
The print management software maker faced a wave of attacks in 2023 aimed at higher education customers.
By David Jones • Updated Sept. 1, 2026 -
 Eric Geller/Cybersecurity Dive
CISA identifies security hurdles that led to very different results in two red-team engagements
The agency said its recent simulated cyberattacks offered several key lessons for many organizations.
By Eric Geller • Aug. 28, 2026 -
 Getty Images
Researchers warn about chained SharePoint sequence
An authentication bypass flaw is already under exploitation, the latest in a series of recent SharePoint attacks.
By David Jones • Updated Aug. 26, 2026 -
tadamichi via Getty Images
CISA orders agencies to fix exploited Zimbra vulnerability
The collaboration software’s developer took almost a full month to patch the flaw after disclosing it.
By Eric Geller • Aug. 25, 2026 -
 Getty Images
Microsoft discloses maximum severity flaw in Entra ID
The company said the remote-code execution vulnerability has been fully mitigated and no further action is necessary.
By David Jones • Aug. 21, 2026 -
 Getty Images
AI-backed campaign targeting vulnerable Siemens S7 devices, CISA and FBI warn
Hackers are developing scripts disguised as legitimate software in attacks aimed at multiple industries, including energy and water.
By David Jones • Updated Aug. 20, 2026
 Previous

