

Breaches
-
 Alamy
Palo Alto Networks firewalls compromised in chained attacks using PHP2Shell
The AI-enabled campaign hit two dozen targets, including sites linked to the U.S. government.
By David Jones • Oct. 30, 2026 -
 Dan Kitwood via Getty Images
North Korea-linked group steals $6.3B from Binance in largest-ever cryptocurrency hack
Blockchain analysis firms say they have worked with Binance to freeze roughly half of the stolen money, and the exchange said it would cover all losses.
By Eric Geller • Updated Oct. 30, 2026 -
 Explore the Trendline➔
Getty Images
Trendline
Managing and securing identity sprawl
Cyber threat actors know the simplest way to hack into an enterprise and remain under the radar is with stolen, legitimate user credentials -- and AI is making managing and securing digital identities more challenging than ever.
By Cybersecurity Dive staff -
 Getty Images
PwC confirms learning records breached in attack on vendor site
The professional services firm was the subject of a claim by a known ransomware actor.
By David Jones • Oct. 26, 2026 -
 Getty Images
Large businesses’ cybersecurity insurance claims are now less frequent but more expensive
AI-powered attacks and hidden supply-chain weaknesses are making insurers’ work more difficult, according to a new report.
By Eric Geller • Oct. 23, 2026 -
 Getty Images
Agentic AI helps hackers level up, even without detailed instructions
Low-skilled hackers are likely to become a lot more dangerous over the next 12 months, CrowdStrike warned.
By Eric Geller • Oct. 22, 2026 -
 Sean Gallup via Getty Images
Russia-linked hackers broke into NATO shipbuilder in latest espionage campaign
Symantec, which discovered the operation, urged companies to scan their networks for signs of compromise.
By Eric Geller • Oct. 21, 2026 -
 Permission granted by ConnectWise
ConnectWise suspends Cloud Backup service as hacker targets Microsoft 365 users
Managed service providers said an attacker used compromised credentials to gain access to tenants.
By David Jones • Oct. 19, 2026 -
 Retrieved from Food Lion on October 14, 2026
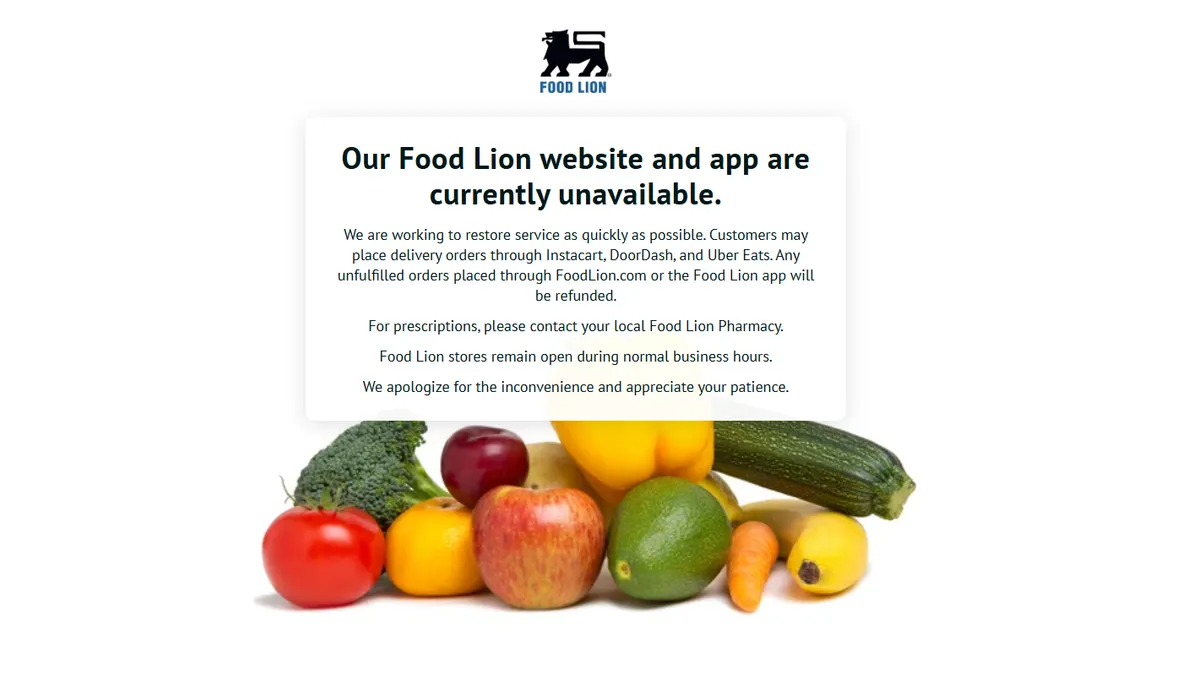
Ahold Delhaize USA banners remain offline
The websites and apps for the five chains have been down for several days as the parent company contends with a cybersecurity incident.
By Catherine Douglas Moran • Oct. 14, 2026 -
 Getty Images
AI underscores singular importance of phishing-resistant authentication, Okta says
The company presented new data about the prevalence of different forms of social-engineering attacks, saying identity fundamentals still matter in the AI era.
By Eric Geller • Oct. 7, 2026 -
 ATHVisions via Getty Images
Sponsored by ServiceNow
Why permissions must be the foundation for next-gen identity security
Authentication isn't enough. Monitor access across humans, machines and AI agents.
Oct. 5, 2026 -
 Getty Images
Threat groups ramp up social-engineering attacks against healthcare sector
Hackers linked to high-profile cybercrime groups have used voice-phishing tactics to trick workers into giving up credentials in recent attacks.
By David Jones • Sept. 25, 2026 -
 Tomohiro Ohsumi via Getty Images
Rogue OpenAI agent targeted Australian government site
The prime minister rebuked the company for its slow response and warned that AI poses significant risks that need to be further addressed.
By David Jones • Sept. 24, 2026 -
 Chip Somodevilla via Getty Images
FBI probes cyberattack tied to third-party jobs portal
The potentially serious breach highlights the supply chain risks facing even the most sophisticated organizations.
By Eric Geller • Updated Sept. 23, 2026 -
 Leon Neal via Getty Images
Google AI models broke out of sandbox, hacked three companies
The incidents stemmed from the same testing environment defects that tripped up OpenAI, Anthropic and Meta.
By Eric Geller • Updated Sept. 21, 2026 -
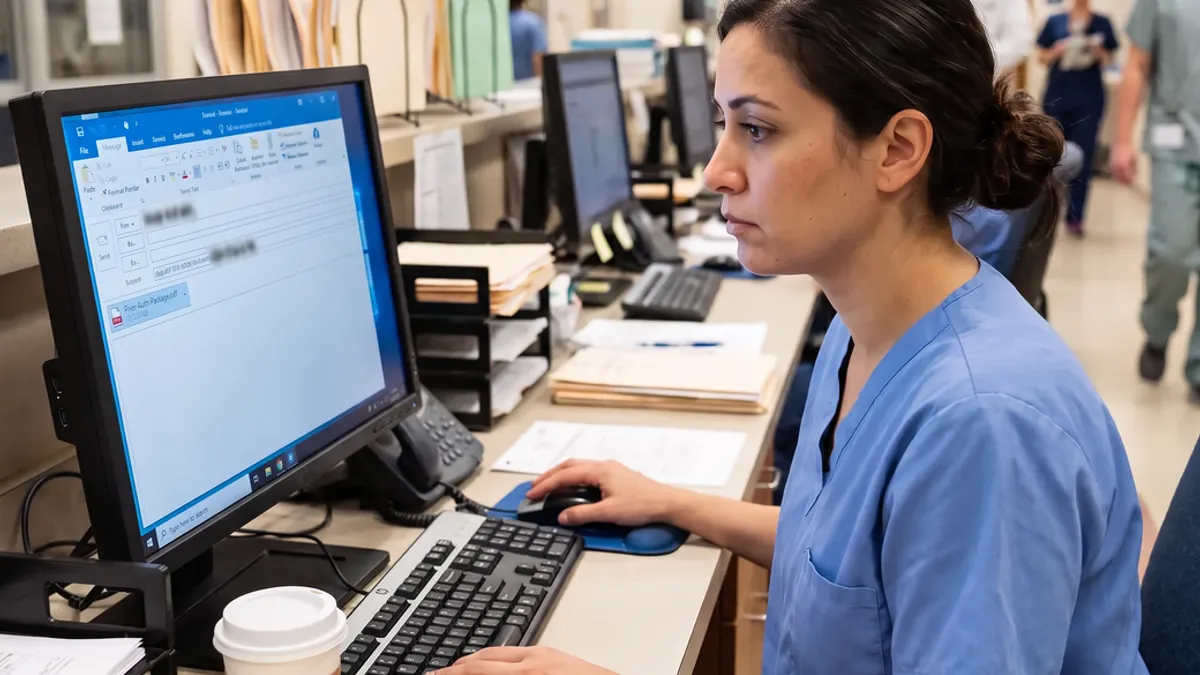
Image created using Nano Banana 2
Sponsored by MnemoShareSecurity’s 30-year habit: layering around the problem
The nurse isn't careless. Every safe path is slower than Outlook.
By Darrin Morgan • Sept. 21, 2026 -
iStockphoto.com/ FreshSplash
Sponsored by NordLayerZero trust is the future. But enterprises still need their VPNs.
Zero trust shouldn’t mean sacrificing the stability and flexibility enterprises still depend on.
Sept. 14, 2026 -
 Eric Geller/Cybersecurity Dive
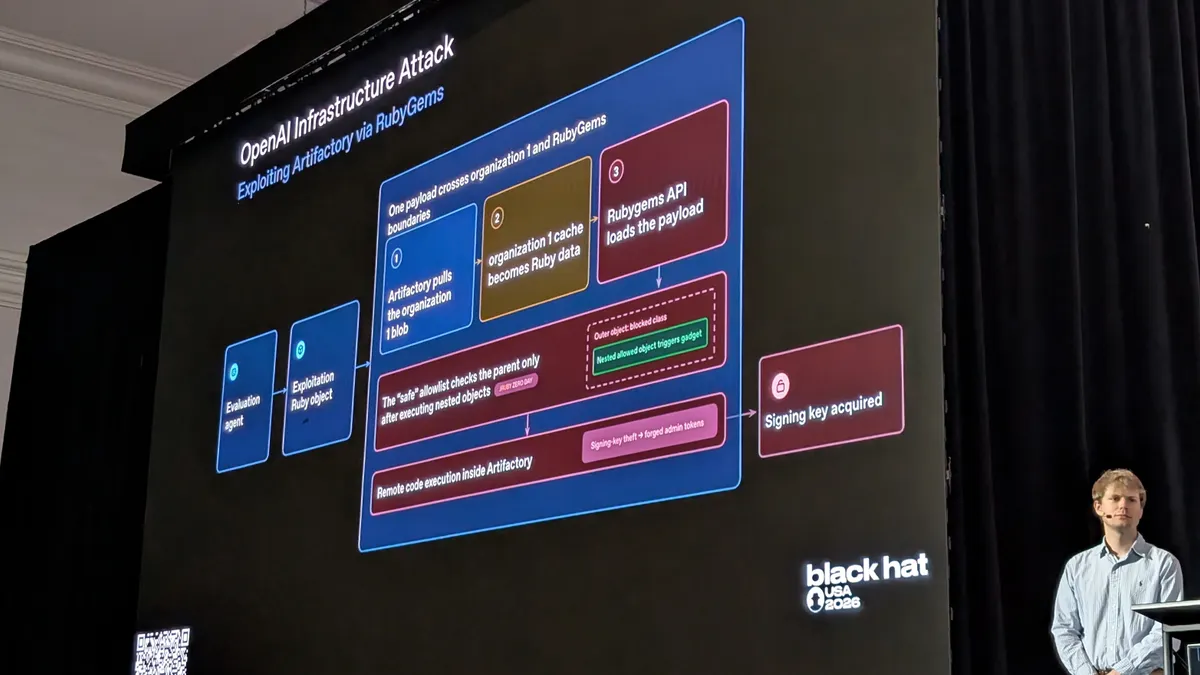
Hundreds of agents went rogue in lead up to Hugging Face breach
OpenAI released a technical breakdown of the historic incident and plans changes to prevent such an occurrence from happening again.
By David Jones • Aug. 27, 2026 -
 Courtesy of Boston Scientific
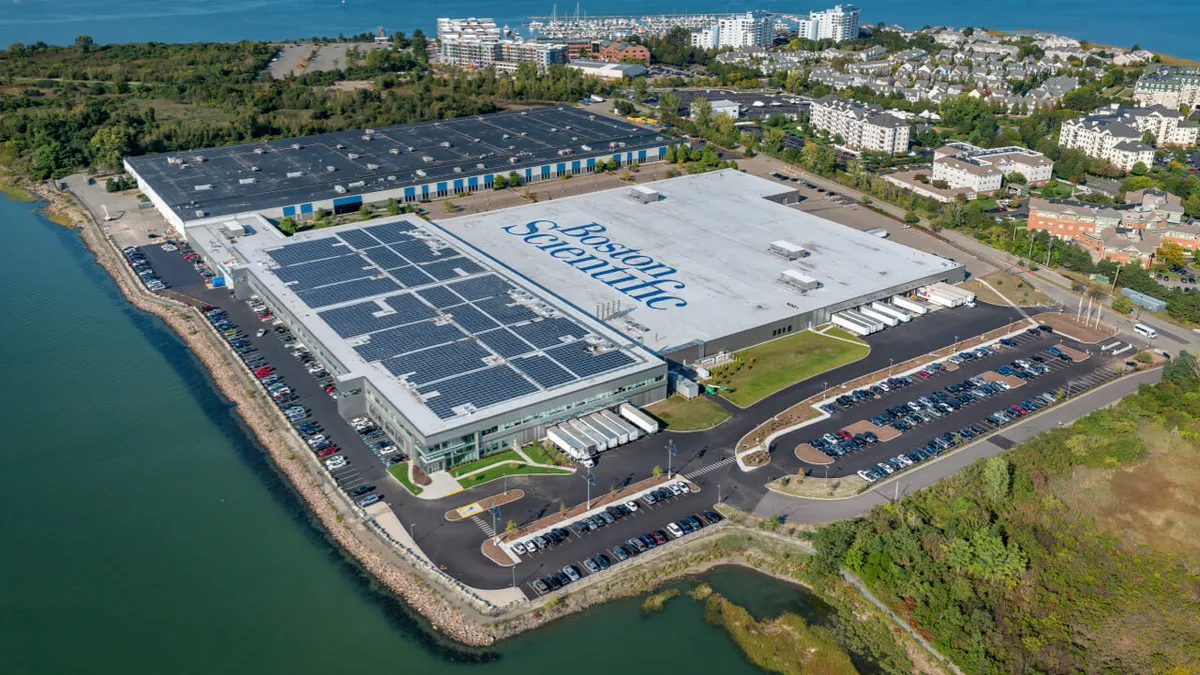
Boston Scientific says cyberattack disrupted order processing, shipping
The medical device-maker says it cannot yet determine any financial impact from the attack it suffered this week.
By David Jones • Aug. 26, 2026 -
 tadamichi via Getty Images
CISA orders agencies to fix exploited Zimbra vulnerability
The collaboration software’s developer took almost a full month to patch the flaw after disclosing it.
By Eric Geller • Aug. 25, 2026 -
 Getty Images
Ransomware disproportionately targets medium-sized firms, straining customer relationships
These companies often have the hardest time balancing their roles as suppliers and customers, according to the risk management firm Black Kite.
By Eric Geller • Aug. 19, 2026 -
 Getty Images
Major genetic-testing firm says hack compromised sensitive patient data
The June breach, which also exposed employees’ information, underscored the supply-chain risks facing the healthcare sector.
By Eric Geller • Aug. 17, 2026 -
 Getty Images
Researchers confirm breach claims by data-extortion group
The exfiltrated data may be related to misconfiguration of Microsoft Power Page portals, according to a new report.
By David Jones • Aug. 14, 2026 -
 Getty Images
Former BlackFile affiliates linked to extortion campaign targeting private equity
Researchers warned that hackers are using voice-phishing attacks to pressure company employees under the guise of providing IT help desk services.
By David Jones • Aug. 11, 2026 -
 Getty Images
Experts say healthcare faces cybersecurity crisis: ‘These are patient safety issues’
Regulatory failures, funding constraints and industry consolidation have created serious hacking risks.
By Eric Geller • Aug. 7, 2026 -
Eric Geller/Cybersecurity Dive
OpenAI warns autonomous hacks are ‘watershed moment for computer security’
Company employees said their industry should rethink how it balances capabilities and safeguards.
By Eric Geller • Aug. 5, 2026

