Policy & Regulation
-
 Getty Images
Government lacks ability to verify AI labs’ claims, experts say
A new survey of national security practitioners identified a wide range of near- and medium-term AI risks for policymakers to consider.
By Eric Geller • Sept. 3, 2026 -
 Eric Geller/Cybersecurity Dive
CISA scraps 6 free cybersecurity assessments for critical infrastructure operators
The agency’s decision, spurred by workload concerns, could leave organizations without valuable insights into their vulnerabilities.
By Eric Geller • Updated Sept. 3, 2026 -
 Explore the Trendline➔
Getty Images
Trendline
AI
AI has boosted cyber threat actors, but it’s also given defenders new tools. Which side will prevail?
By Cybersecurity Dive staff -
 Getty Images
Federal authorities disrupt China-backed hacking operation targeting US critical infrastructure
Compromised IoT devices were used in a yearslong campaign against key sectors and federal agencies.
By David Jones • Aug. 27, 2026 -
 Chip Somodevilla via Getty Images
Treasury to help financial firms transition to quantum-resistant encryption
The government is concerned that hackers could someday decrypt financial information and other secrets using code-breaking quantum computers.
By Eric Geller • Aug. 26, 2026 -
 Courtesy of National Cyber Security Centre
UK power facility disabled for days after suspected state-linked cyberattack
The disruption took place amid a wave of attacks targeting vulnerable industrial devices in the water and energy sectors.
By David Jones • Aug. 24, 2026 -
 Getty Images
House Democrats ask GAO to study CISA workforce cuts
Five lawmakers serving on the Homeland Security Committee said Congress didn’t know enough about the Trump administration’s changes to the cybersecurity agency.
By Eric Geller • Aug. 24, 2026 -
 Getty Images
Defense contractors still struggling with basic CMMC requirements
A “confidence disconnect” is plaguing the industry, a consulting firm said.
By Eric Geller • Aug. 21, 2026 -
 Getty Images
What we know so far about the hacking campaign against US water systems
Support is growing for stricter oversight and increased financial resources for utilities in the wake of a cyberattack spree, suspected to be the work of Iran-linked threat groups.
By David Jones • Aug. 20, 2026 -
 Getty Images
AI-backed campaign targeting vulnerable Siemens S7 devices, CISA and FBI warn
Hackers are developing scripts disguised as legitimate software in attacks aimed at multiple industries, including energy and water.
By David Jones • Updated Aug. 20, 2026 -
 Getty Images
DOJ charges 17 people in Iran-backed hacking campaign against US
Officials allege an IRGC-linked organization was behind a coordinated effort to steal research from American universities, companies and government agencies.
By David Jones • Updated Aug. 19, 2026 -
 Chip Somodevilla via Getty Images
Deep Dive
AI-powered vulnerability clearinghouse faces deep skepticism, major challenges
The U.S. government’s promises about the Gold Eagle coordination program are overblown, experts said, but the initiative could help organizations prioritize patching and mitigation.
By Eric Geller • Aug. 18, 2026 -
 Getty Images
Deep Dive
CVE Program eyes automation and globalization to weather AI ‘vulnpocalypse’
The vulnerability coordination project has had a rocky few years, but a key leader says it will “flourish and improve.”
By Eric Geller • Aug. 11, 2026 -
 Getty Images
Experts say healthcare faces cybersecurity crisis: ‘These are patient safety issues’
Regulatory failures, funding constraints and industry consolidation have created serious hacking risks.
By Eric Geller • Aug. 7, 2026 -
 Eric Geller/Cybersecurity Dive
AI firms know policymakers won’t ‘let you make a Terminator factory,’ DHS official says
The Trump administration believes leading AI companies have learned important lessons from recent incidents and regulation isn’t necessary to preserve those lessons.
By Eric Geller • Aug. 7, 2026 -
 Eric Geller/Cybersecurity Dive
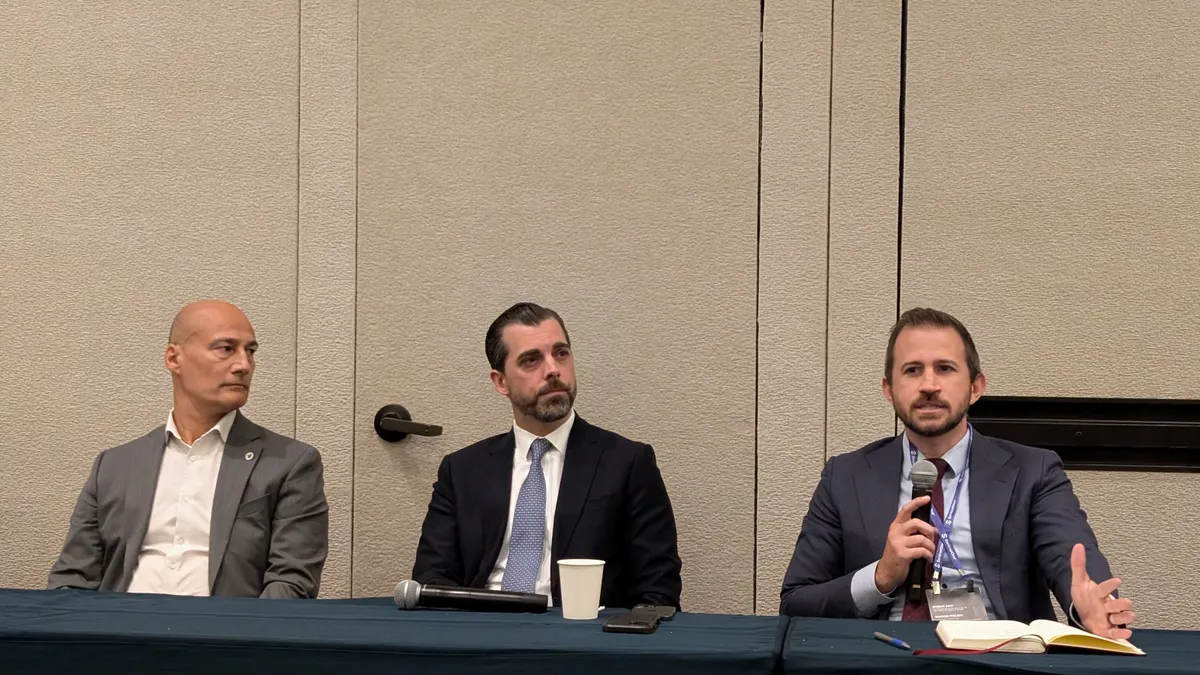
Western government leaders call for a focus on infrastructure resilience, not AI hype
U.S. and allied officials said companies should start preparing now for a cyberattack that changes how they provide essential services.
By Eric Geller • Aug. 5, 2026 -
 Courtesy of Billington
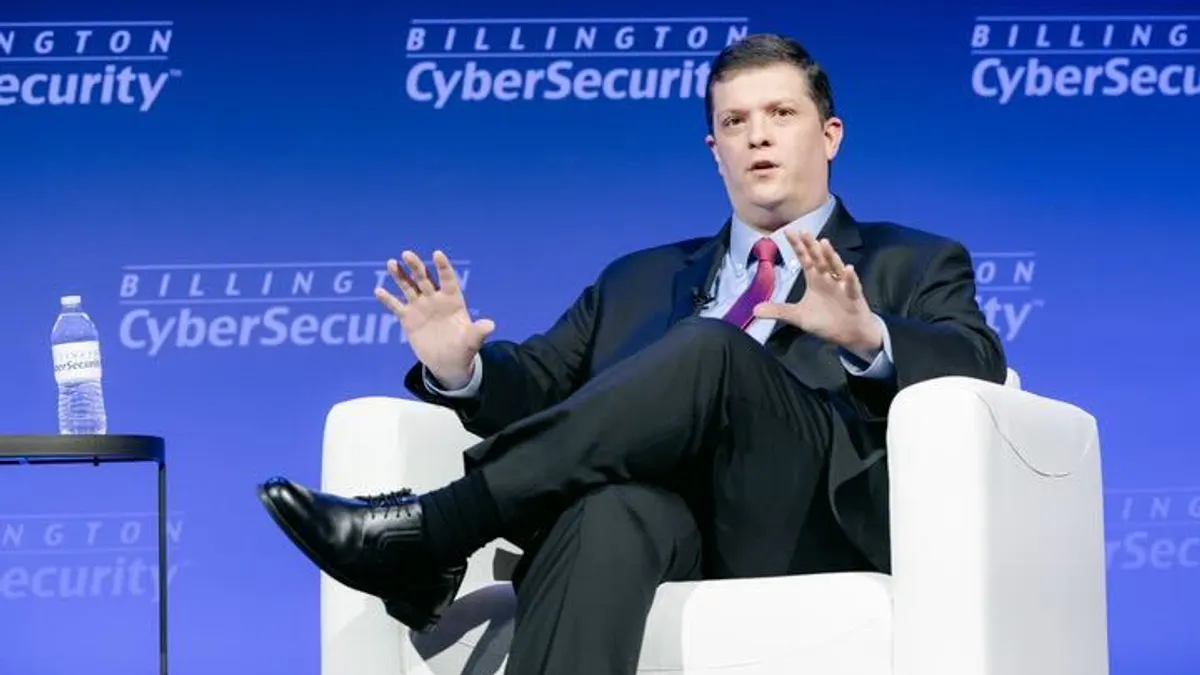
CISA is prioritizing work with critical infrastructure as it begins to recover from cuts
The agency has been focused on helping secure systems at drinking and wastewater utilities in recent weeks.
By David Jones • Aug. 5, 2026 -
 Permission granted by Billington
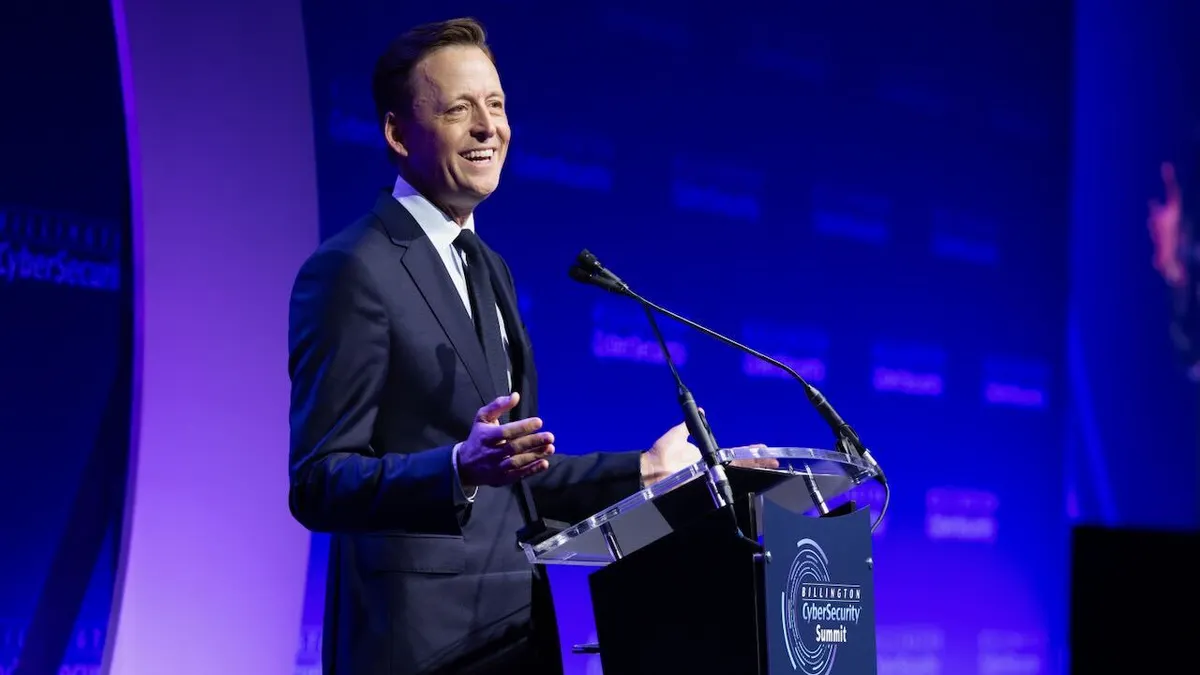
White House walks tightrope on securing AI without stifling tech innovation
National Cyber Director Sean Cairncross said the administration wants to work collaboratively with the private sector.
By David Jones • Aug. 5, 2026 -
 Getty Images
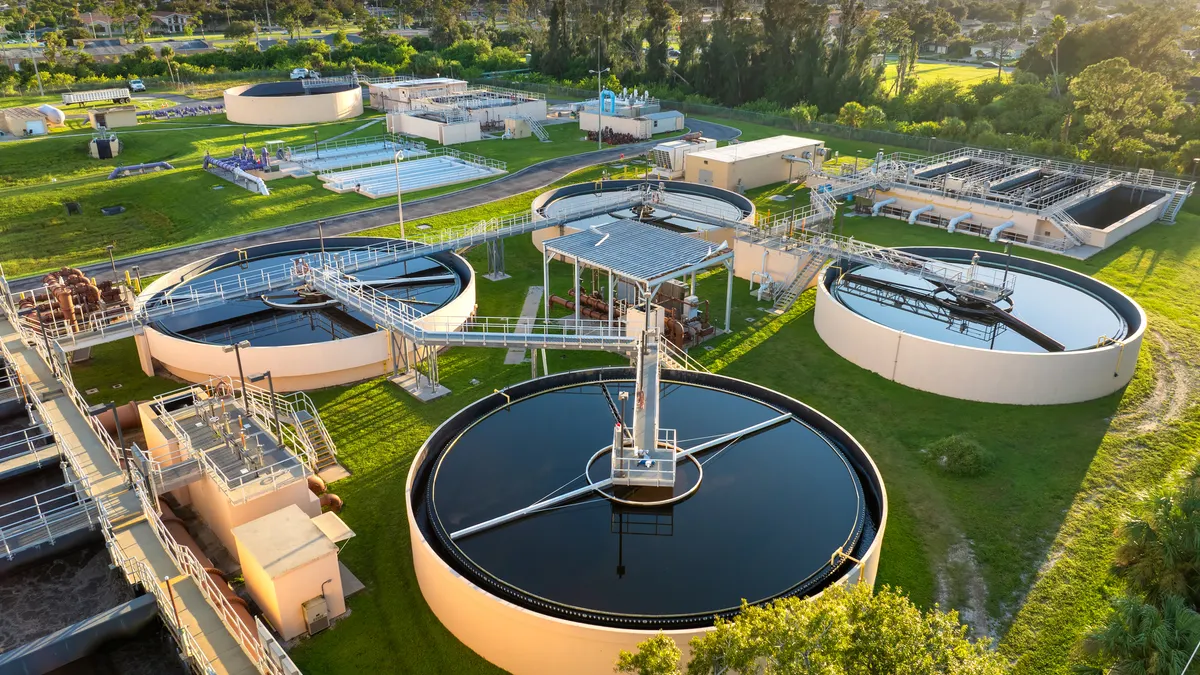
OT security coalition urges Congress, CISA to enact reforms amid water sector hacks
Iran-nexus hackers are suspected in a broad campaign targeting drinking and wastewater sites in at least seven U.S. states.
By David Jones • Aug. 3, 2026 -
 Getty Images
US authorities see ‘significant escalation’ in attacks on water system devices
Hackers have locked operators out of their own OT networks, modified passwords and changed IP addresses.
By David Jones • July 31, 2026 -
 Stephen Maturen via Getty Images
Authorities investigating a coordinated cyberattack against Minnesota water systems
The two-day attack comes days after federal officials warned of state-linked threat groups targeting a wider set of industrial devices.
By David Jones • Updated July 29, 2026 -
 Getty Images
Tech industry giants say US must embrace openness, transparency in AI
Open-source and open-weight AI models are essential cybersecurity tools, two groups of major AI and security firms said.
By Eric Geller • July 27, 2026 -
 Michael Gruber via Getty Images
CISA, FBI warn that Iran-linked hackers are expanding target set for water, energy
The agencies said threat groups have disrupted critical infrastructure sites by exploiting vulnerable PLC devices.
By David Jones • July 23, 2026 -
 Retrieved from GAO.
GAO report details scope of cybersecurity regulation overlap
A morass of rules is forcing companies to report the same information multiple times — and sometimes, those rules conflict.
By Eric Geller • July 23, 2026 -
 Jim Vondruska via Getty Images
Gaps in network security, oversight strategy hamper US’s aviation cybersecurity regulators
A new government audit identified several weaknesses at the two agencies that protect air travel from hackers.
By Eric Geller • July 16, 2026 -
 Getty Images
Sharp rise in AI adoption for cyber defense exposes major governance gap
A report by the SANS Institute indicates a split between senior security leaders and frontline practitioners.
By David Jones • July 14, 2026