

The Latest
-
 Getty Images
Insurance industry fears potential impacts from PHP2Shell
A systemic cyber event could lead to billions of dollars in claims that exceed current risk models.
Updated Oct. 29, 2026 -
 Makenzie Holland/Cybersecurity Dive
JPMorgan Chase, Goldman Sachs underscore security in AI plans
“This is one of the most important times to make sure you are appropriately balancing risk and innovation,” said JPMorgan Chase Global CIO Lori Beer.
-
 Getty Images
Hackers seize on vulnerable IoT devices to spy, pivot and route traffic
Known vulnerabilities with available patches are by far the biggest risk facing connected devices, a new report found.
-
 Getty Images
CISA, security researchers confirm successful exploitation of PHP flaws
The security community has come under increased scrutiny as earlier threat warnings were slow to materialize.
-
 Getty Images
US launches program to deliver free cybersecurity help to rural hospitals
Small and rural healthcare organizations are among the most vulnerable critical infrastructure organizations in the nation.
-
 Getty Images
PwC confirms learning records breached in attack on vendor site
The professional services firm was the subject of a claim by a known ransomware actor.
-
 Eric Geller/Cybersecurity Dive
CISA promises proactive defense in new strategic plan
The beleaguered agency, still recovering from major workforce cuts, promised to deepen partnerships and stay ahead of evolving threats.
-
 Getty Images
PHP exploitation moves at slower-than-expected pace, but millions remain at risk
Security researchers flag botnet activity, but successful compromises have yet to break through.
Updated Oct. 26, 2026 -
 Getty Images
Large businesses’ cybersecurity insurance claims are now less frequent but more expensive
AI-powered attacks and hidden supply-chain weaknesses are making insurers’ work more difficult, according to a new report.
-
 Getty Images
China-nexus actor linked to attack on ConnectWise Cloud Backup
Researchers said the hackers employed a powerful AI tool to accelerate and scale the attacks against hundreds of Microsoft 365 users.
-
 Getty Images
Agentic AI helps hackers level up, even without detailed instructions
Low-skilled hackers are likely to become a lot more dangerous over the next 12 months, CrowdStrike warned.
-
 Getty Images
Critical PHP vulnerabilities expose most websites to potential compromise
Government agencies urged organizations to take their sites offline until they could be fixed.
Updated Oct. 21, 2026 -
 Getty Images
Weak encryption certificates could have let hackers easily spoof websites
Major web browsers blocked the eMudhra TLS certificates to prevent them from being weaponized.
-
 Permission granted by Ingram Micro
FBI, CISA warn that SafePay ransomware poses threat to critical infrastructure
The group has been linked to a 2025 attack targeting technology firm Ingram Micro.
-
 Sean Gallup via Getty Images
Russia-linked hackers broke into NATO shipbuilder in latest espionage campaign
Symantec, which discovered the operation, urged companies to scan their networks for signs of compromise.
-
 Matt Kapko/Cybersecurity Dive
Ransomware groups expand targeting of Palo Alto Networks vulnerability
Multiple threat actors have exploited a high-severity flaw in the company’s GlobalProtect portal.
-
 Robert Way via Getty Images
AI security hiring focuses on red-teaming, SOC orchestration and governance
Roles mitigating AI deepfakes and overseeing post-quantum encryption rollouts are on the horizon, according to the SANS Institute.
-
 Getty Images
Boards confident on cybersecurity, AI oversight, but tech changes outpace readiness
Nearly half of corporate directors think board members need cybersecurity expertise, a new survey found.
-
 Permission granted by ConnectWise
ConnectWise suspends Cloud Backup service as hacker targets Microsoft 365 users
Managed service providers said an attacker used compromised credentials to gain access to tenants.
-
 Getty Images
China-nexus espionage actor targets BeyondTrust support tool in zero-day campaign
Researchers say the hacker is harvesting credentials and stealing sensitive information.
Updated Oct. 16, 2026 -
 Getty Images
Open-source security rests on understanding risks, scaling fixes
Developers should coordinate security work to make the most of their interconnected ecosystem, IBM said in a new report.
-
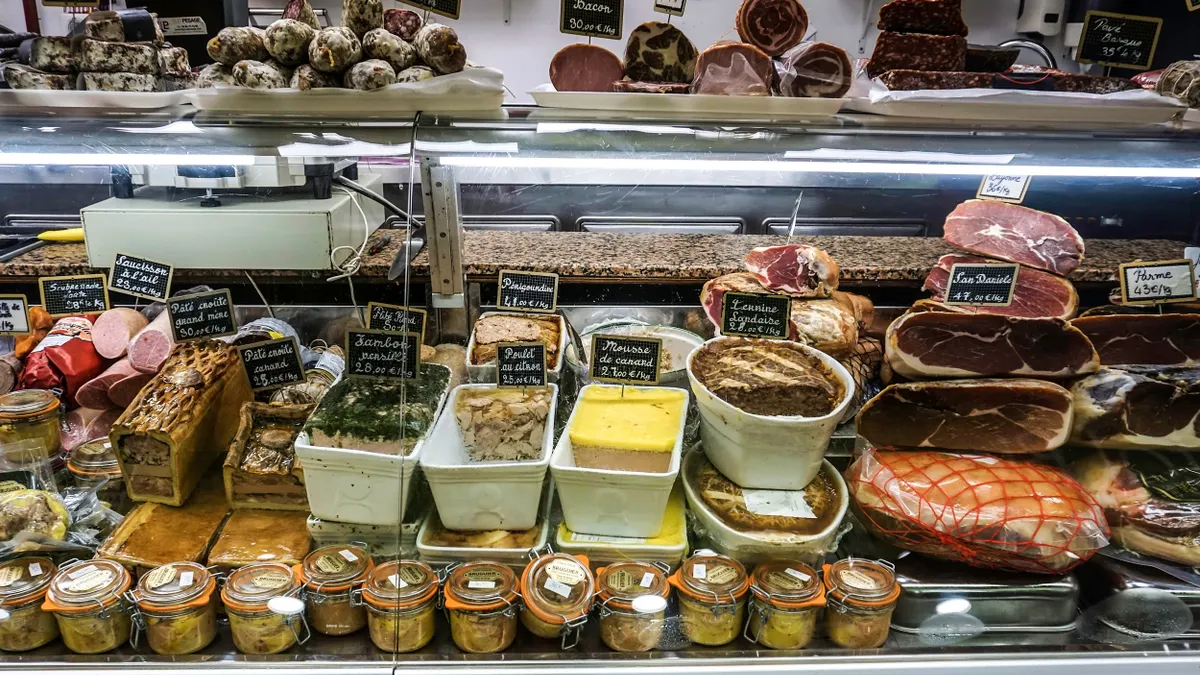 Alamy
Thousands of refrigerator devices remain exposed following French cyberattack
The investigation points to a much wider risk for industrial systems across the globe.
Updated Oct. 15, 2026 -
 Getty Images
Internet exposure of AI tools, ICS devices continues to grow
Vulnerability disclosures and hacking campaigns haven’t made much of a dent in the amount of important infrastructure left online, a new report found.
-
 Devrimb
Hacker targets Ivanti Connect Secure in chained exploitation
Researchers warn the attacker is taking multiple steps to clean up forensic evidence after an attack.
-
 Carl Court via Getty Images
Feds crack down on North Korean IT-worker schemes with new raids, charges and arrests
The latest operation targeted “laptop farms” across Texas that allegedly aided North Korea’s moneymaking plots.

