Vulnerability
-
 Getty Images
PHP exploitation moves at slower-than-expected pace, but millions remain at risk
Security researchers flag botnet activity, but successful compromises have yet to break through.
By David Jones • Oct. 23, 2026 -
 Getty Images
Weak encryption certificates could have let hackers easily spoof websites
Major web browsers blocked the eMudhra TLS certificates to prevent them from being weaponized.
By Eric Geller • Oct. 21, 2026 -
 Explore the Trendline➔
Getty Images
Trendline
Vulnerability Management
The rapid advancement Ai has changed the debate over secure software in the entrprise.
By Cybersecurity Dive staff -
 Getty Images
Critical PHP vulnerabilities expose most websites to potential compromise
Government agencies urged organizations to take their sites offline until they could be fixed.
By Eric Geller • Updated Oct. 21, 2026 -
 Matt Kapko/Cybersecurity Dive
Ransomware groups expand targeting of Palo Alto Networks vulnerability
Multiple threat actors have exploited a high-severity flaw in the company’s GlobalProtect portal.
By David Jones • Oct. 20, 2026 -
 Permission granted by HPE
Sponsored by HPE
Hybrid mesh firewalls: Distributed security enforcement for a self-driving network
Can traditional firewalls keep up with today's distributed enterprise? Discover how hybrid mesh firewalls close security gaps without slowing networks.
Oct. 19, 2026 -
 Getty Images
China-nexus espionage actor targets BeyondTrust support tool in zero-day campaign
Researchers say the hacker is harvesting credentials and stealing sensitive information.
By David Jones • Updated Oct. 16, 2026 -
 Getty Images
Open-source security rests on understanding risks, scaling fixes
Developers should coordinate security work to make the most of their interconnected ecosystem, IBM said in a new report.
By Eric Geller • Oct. 16, 2026 -
 Alamy
Thousands of refrigerator devices remain exposed following French cyberattack
The investigation points to a much wider risk for industrial systems across the globe.
By David Jones • Updated Oct. 15, 2026 -
 Getty Images
Internet exposure of AI tools, ICS devices continues to grow
Vulnerability disclosures and hacking campaigns haven’t made much of a dent in the amount of important infrastructure left online, a new report found.
By Eric Geller • Oct. 15, 2026 -
 Devrimb
Hacker targets Ivanti Connect Secure in chained exploitation
Researchers warn the attacker is taking multiple steps to clean up forensic evidence after an attack.
By David Jones • Oct. 14, 2026 -
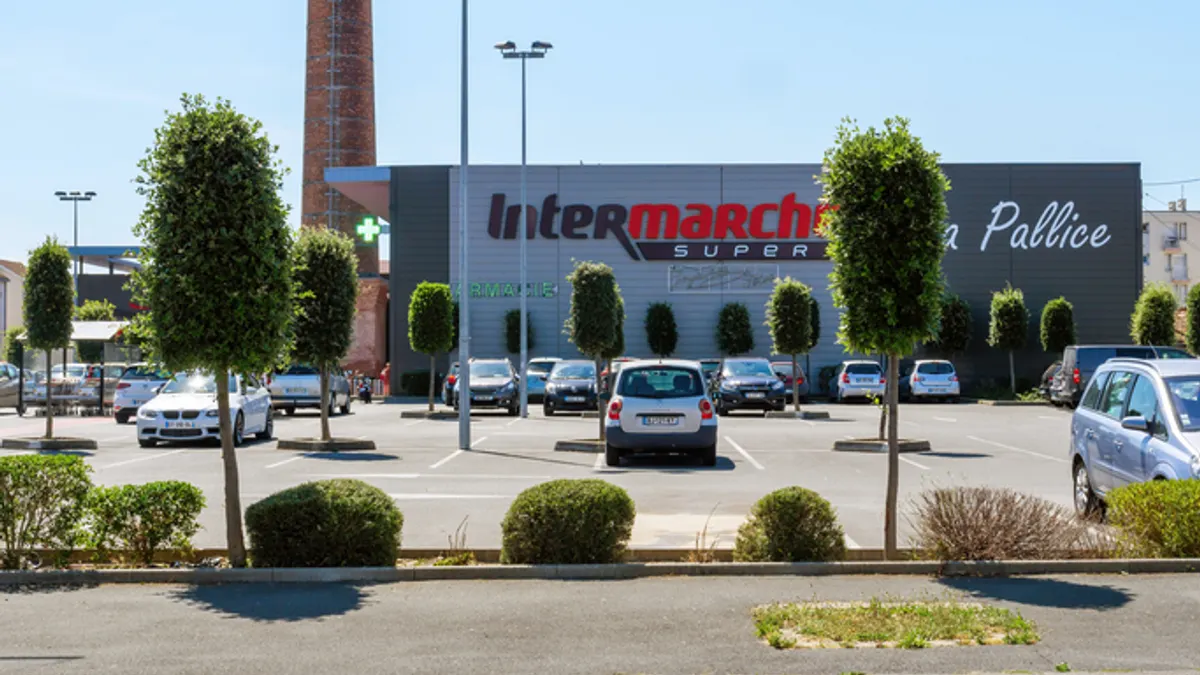 AdrianHancu via Getty Images
Dangerous flaws in refrigeration equipment were disclosed months before retail attacks
Hundreds of French supermarkets faced a sophisticated cyberattack, allowing hackers to manipulate industrial controls.
By David Jones • Updated Oct. 13, 2026 -
Citrix via Flickr
CISA calls on Citrix NetScaler customers to patch as new flaws disclosed
A newly discovered critical vulnerability is adding to the workload of customers mitigating other recent flaws.
By David Jones • Updated Oct. 12, 2026 -
 Getty Images
GitLab fixes critical vulnerability that exposed software environments to sabotage
The company urged customers to upgrade to the latest versions of its flagship products.
By Eric Geller • Oct. 12, 2026 -
 Sean Gallup / Staff via Getty Images
IBM’s AI-powered vulnerability clearinghouse finds hundreds of Java flaws
The tech giant’s announcement underscores the insufficiency of companies’ existing software supply chain security practices.
By Eric Geller • Oct. 6, 2026 -
Citrix via Flickr
Citrix issues patch for third exploited flaw in NetScaler
The memory overflow vulnerability could lead to a denial-of-service condition under certain circumstances.
By David Jones • Updated Oct. 5, 2026 -
 Courtesy of Fortinet
Fortinet warns that critical flaw in FortiMail is facing exploitation
Security researchers said that attackers can gain access to credentials, stored mail and other connected systems.
By David Jones • Oct. 2, 2026 -
 Justin Sullivan via Getty Images
Mass exploitation of Citrix NetScaler: What we currently know
Suspected state-linked actors targeted critical vulnerabilities in the widely used platform, causing widespread disruption across Europe and North America.
By David Jones • Sept. 30, 2026 -
 Justin Sullivan/Getty Images via Getty Images
Citrix NetScaler exploitation began days before public notification
Customers need to check systems for compromise prior to patching, because the security upgrade may not fully resolve an infected system.
By David Jones • Updated Sept. 29, 2026 -
 Getty Images
Kiteworks lifts advisory after precautionary warning for customers to shut down systems
The firm had received information from law enforcement of a possible attack.
By David Jones • Sept. 28, 2026 -
Citrix via Flickr
Citrix urges immediate upgrades of NetScaler amid widespread exploitation attempts
Security teams received urgent calls to disconnect servers before authorities confirmed critical zero-day flaws.
By David Jones • Sept. 28, 2026 -
 Asanka Ratnayake via Getty Images
Niche AI tools pose major cybersecurity risk to infrastructure operators
Security vetting tools and processes weren’t designed with obscure AI services in mind, according to TrendAI.
By Eric Geller • Sept. 28, 2026 -
 Courtesy of Wiz
Wiz uses AI to find vulnerabilities in critical infrastructure
The Google subsidiary, which helped a railroad and two hospitals, invited others to apply for its free scanning service.
By Eric Geller • Sept. 24, 2026 -
 Getty Images
Insurance sector begins to offer clarity on AI-related cyber claims
The emergence of agentic AI and frontier models has led to widespread uncertainty for policyholders.
By David Jones • Sept. 22, 2026 -
 Getty Images
China-nexus actor steals thousands of documents in monthslong exploitation campaign
Researchers suspect the hacker employed LLMs to develop custom tools.
By David Jones • Sept. 21, 2026 -
 Permission granted by Arctic Wolf
Sponsored by Arctic Wolf
More CVEs than ever. The same old ones keep getting exploited.
Vulnerability volume is climbing fast. The exploited ones are old and already patchable.
Sept. 21, 2026