Threats: Page
-
 Getty Images
Network edge devices still widely used after reaching end-of-life status
A report by VulnCheck shows nation-state hackers often target flaws in aging routers, firewalls and VPNs.
By David Jones • March 23, 2026 -
 Sean Gallup/Getty Images via Getty Images
US, allies move to dismantle four high-volume IoT botnets
The armies of hacked computers and internet of things gadgets powered disruption and extortion campaigns that sometimes cost victims tens of thousands of dollars.
By Eric Geller • March 20, 2026 -
 Explore the Trendline➔
Getty Images
Trendline
Securing against ransomware
Security professionals hail cybersecurity basics as the best defense against ransomware — regular patching, multifactor authentication and, maybe most importantly, information sharing.
By Cybersecurity Dive staff -
 Getty Images
DOJ confirms seizure of domains linked to Iran-backed threat actor
A group connected to Iranian intelligence used the same infrastructure to claim credit for the hack of medical technology firm Stryker.
By David Jones • March 20, 2026 -
 pigphoto/iStock/Getty Images Plus via Getty Images
Water utilities need hands-on cybersecurity help, not just free guidance, pilot program finds
In a new report, Microsoft criticized the federal government for scaling back support to critical infrastructure operators.
By Eric Geller • March 19, 2026 -
 Getty Images
CISA urges organizations to harden endpoint security following Stryker attack
The agency is coordinating with the FBI and other agencies amid concerns about additional threat activity involving Microsoft Intune.
By David Jones • March 19, 2026 -
 Getty Images
Threat groups target cyber-physical systems to disrupt critical infrastructure providers
The Iran war has raised concerns that key industrial sectors could be the target of hacktivists, state actors and other groups.
By David Jones • March 18, 2026 -
 vchal/iStock /Getty Images Plus via Getty Images
New research unpacks North Korea’s stealthy, sophisticated remote IT worker schemes
The report recommends that businesses practice several forms of vigilance to avoid unwittingly hiring Pyongyang’s operatives.
By Eric Geller • March 18, 2026 -
 Michael M. Santiago via Getty Images
Stryker attack raises concerns about role of device management tool
Researchers warn that Microsoft Intune may have been weaponized to wipe critical devices.
By David Jones • March 16, 2026 -
 Alamy
Stryker’s manufacturing, shipping disrupted after cyberattack
The medtech company says it's still experiencing issues with order processing, manufacturing and shipping.
By Ricky Zipp , David Jones • March 13, 2026 -
 Getty Images
Even primitive AI-coded malware helps hackers move faster, thwart attribution
IBM researchers discovered an autonomously coded backdoor that they called unsophisticated but nonetheless ominous.
By Eric Geller • March 13, 2026 -
 Courtesy of Hexagon
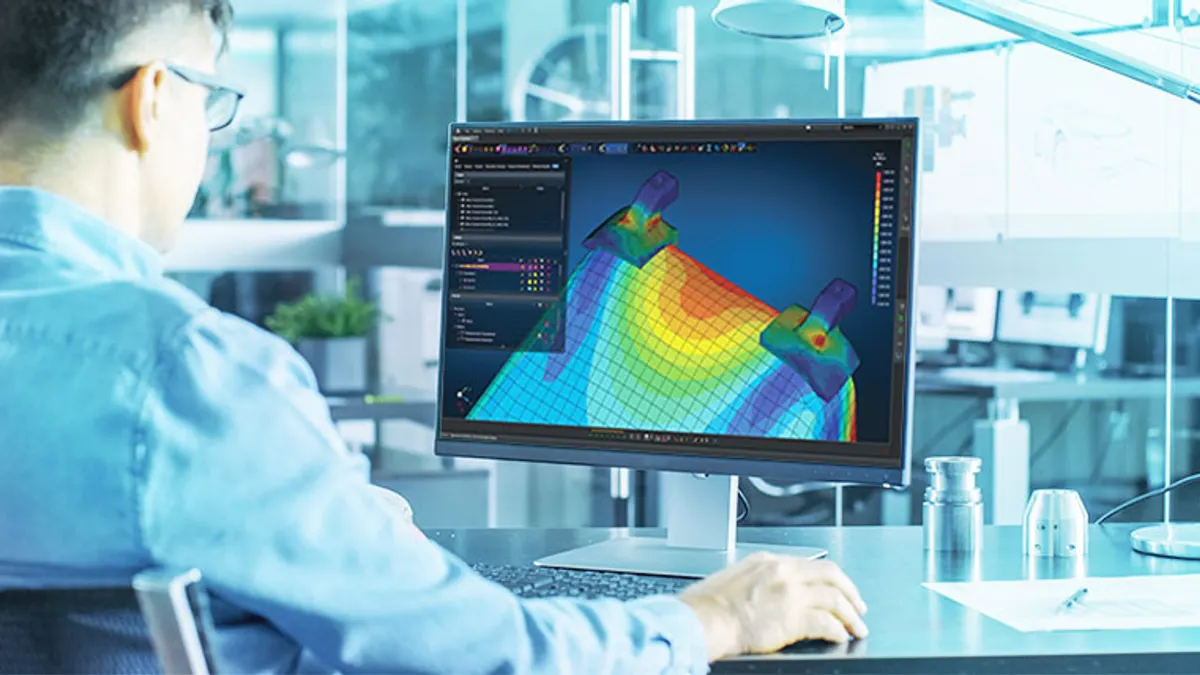
5 ways to protect manufacturing companies from cyberattacks
Manufacturing suffered the most cyberattacks of any industry last year. Experts have advice about hardening networks and avoiding common mistakes.
By Jeff Kinney • March 12, 2026 -
 Retrieved from NASA's Moderate Resolution Imaging Spectroradiometer.
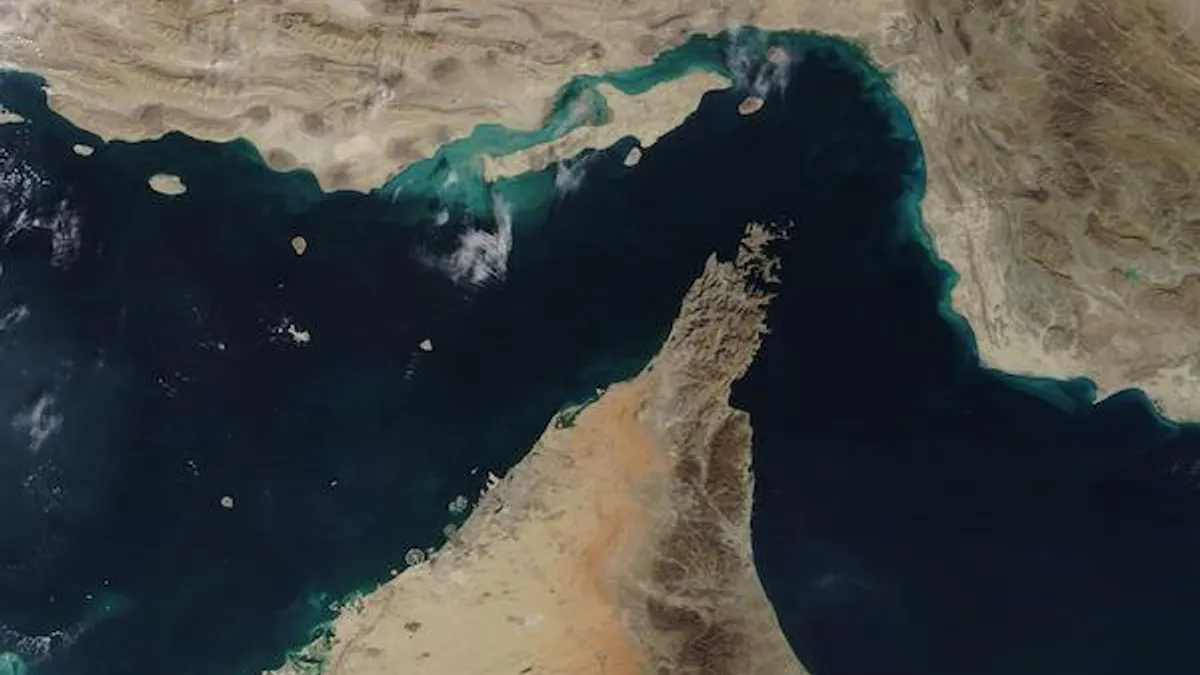
Coalition of information-sharing groups warns of cyber, physical attacks
A joint advisory says Iran-linked groups are targeting U.S. critical infrastructure using DDoS, phishing and other retaliatory techniques.
By David Jones • Updated March 12, 2026 -
 R. Eskalis/NIST. Retrieved from NIST.
Industry to NIST: Keep agentic AI standards flexible and voluntary
The business community said security guidance should reflect the nascency and diversity of the field.
By Eric Geller • March 11, 2026 -
 Michael Gruber via Getty Images
US entities face heightened cyber risk related to Iran war
The military campaign against Iran is putting local governments, critical infrastructure providers and major U.S. companies at heightened risk of disruptive attacks.
By David Jones • March 10, 2026 -
 Majid Saeedi/ via Getty Images
State-linked actors targeted US networks in lead-up to Iran war
Researchers found backdoors installed on U.S. company networks in the weeks prior to the U.S. and Israeli bombing campaign.
By David Jones • March 9, 2026 -
 Alex Wong via Getty Images
HHS adds cybersecurity guidance to healthcare sector self-assessment tool
Organizations can now use the online platform to test their readiness for digital security crises.
By Eric Geller • March 6, 2026 -
 Getty Images
Microsoft, Europol disrupt global phishing platform Tycoon 2FA
The service helped cybercriminals bypass multifactor authentication and led to business email compromise and ransomware.
By David Jones • March 5, 2026 -
 Majid Saeedi via Getty Images
Pro-Russia actors team with Iran-linked hackers in attacks
The groups formed a loose alliance in recent days, targeting critical infrastructure in the Middle East and the U.S.
By David Jones • Updated March 3, 2026 -
Getty Images
Ransomware is now less about malware and more about impersonation
Stolen passwords have replaced infectious code as the most common tactic in major breaches, Cloudflare said.
By Eric Geller • March 3, 2026 -
 Majid Saeedi via Getty Images
Iran-linked hackers raise threat level against US, allies
Security researchers warn that hacktivists and state-linked groups are using DDoS, phishing and other tactics against critical infrastructure.
By David Jones • Updated March 2, 2026 -
 Getty Images
‘Resurge’ malware can remain undetected on devices
CISA previously issued an alert about attacks that exploited a vulnerability in Ivanti Connect Secure.
By David Jones • Updated Feb. 27, 2026 -
 peshkov via Getty Images
AI accelerates lateral movement in cyberattacks
New research paints a grim picture of how the technology is making cyberattacks faster and easier for threat actors.
By Eric Geller • Feb. 26, 2026 -
 Getty Images
CISA orders agencies to patch Cisco devices now under attack
The vulnerabilities, scored as critical, affect the company’s software-defined wide-area networking (SD-WAN) systems.
By Eric Geller • Feb. 25, 2026 -
 Kevin Frayer via Getty Images
China-linked hackers breached dozens of telecoms, government agencies
The cyberattacks used a clever technique: malware that hid in plain sight on Google Sheets.
By Eric Geller • Feb. 25, 2026 -
 Getty Images
In the AI era, CISOs worry about data leaks and doubt tech will solve skills gaps
CISOs see AI as necessary but insufficient technology and fraught with risks, a new report found.
By Eric Geller • Feb. 24, 2026
 Previous