Cyberattacks
-
 Tomohiro Ohsumi via Getty Images
US cyber resilience, oversight tested in series of attacks
Attacks targeting key industrial sites and unforced errors among leading AI companies are raising alarm bells.
By David Jones • Oct. 6, 2026 -
 Getty Images
Sponsored by Thales Cybersecurity
Modernizing data security with DSPM, AI and fewer tools
For organizations, the proper safeguards—such as controls or restrictions—must be put in place.
Oct. 5, 2026 -
 Explore the Trendline➔
Getty Images
Trendline
Incident Response
How organizations respond to attacks is changing as the threat environment shifts dramatically.
By Cybersecurity Dive staff -
 Getty Images
Defending against AI-fueled cyberattacks requires focus on identity, data governance, Microsoft says
The company’s latest report previews how AI is changing threat activity, including by automating ransomware attacks.
By Eric Geller • Oct. 2, 2026 -
 Eric Geller/Cybersecurity Dive
National cyber director defends private-sector hacking program, urges focus on security basics
Letting businesses help the government deter cybercrime will benefit all Americans, Sean Cairncross said.
By Eric Geller • Sept. 30, 2026 -
 Permission granted by and created by Picus Design Team
Sponsored by Picus Security
Security testing has to keep pace with AI-driven attackers
AI attackers move at machine speed. Security validation needs to follow every meaningful change.
By Sila Ozeren Hacioglu, Security Research Engineer at Picus Security. • Sept. 28, 2026 -
iStockphoto, Milan Jovic
Sponsored by NordLayer Intelligence by NordStellarYour attack surface is bigger than you think… and hackers know that
Cyberattacks are exploiting trusted access points like compromised credentials and session cookies. Discover how organizations are gaining visibility beyond their perimeter to stay ahead of threats.
Sept. 28, 2026 -
 Chip Somodevilla via Getty Images
FBI probes cyberattack tied to third-party jobs portal
The potentially serious breach highlights the supply chain risks facing even the most sophisticated organizations.
By Eric Geller • Updated Sept. 23, 2026 -
 Getty Images
Businesses fear cyberattacks more than anything else, driven by AI and supply chain worries
Many companies still aren’t preparing thoroughly enough to face a hack, the insurance firm Travelers said in a new report.
By Eric Geller • Sept. 23, 2026 -
 Leon Neal via Getty Images
Google AI models broke out of sandbox, hacked three companies
The incidents stemmed from the same testing environment defects that tripped up OpenAI, Anthropic and Meta.
By Eric Geller • Updated Sept. 21, 2026 -
 Getty Images
Settra ransomware variant deployed in recent attacks
Security researchers warned that hackers are using VPN credentials for initial access and deploying RMM tools.
By David Jones • Sept. 18, 2026 -
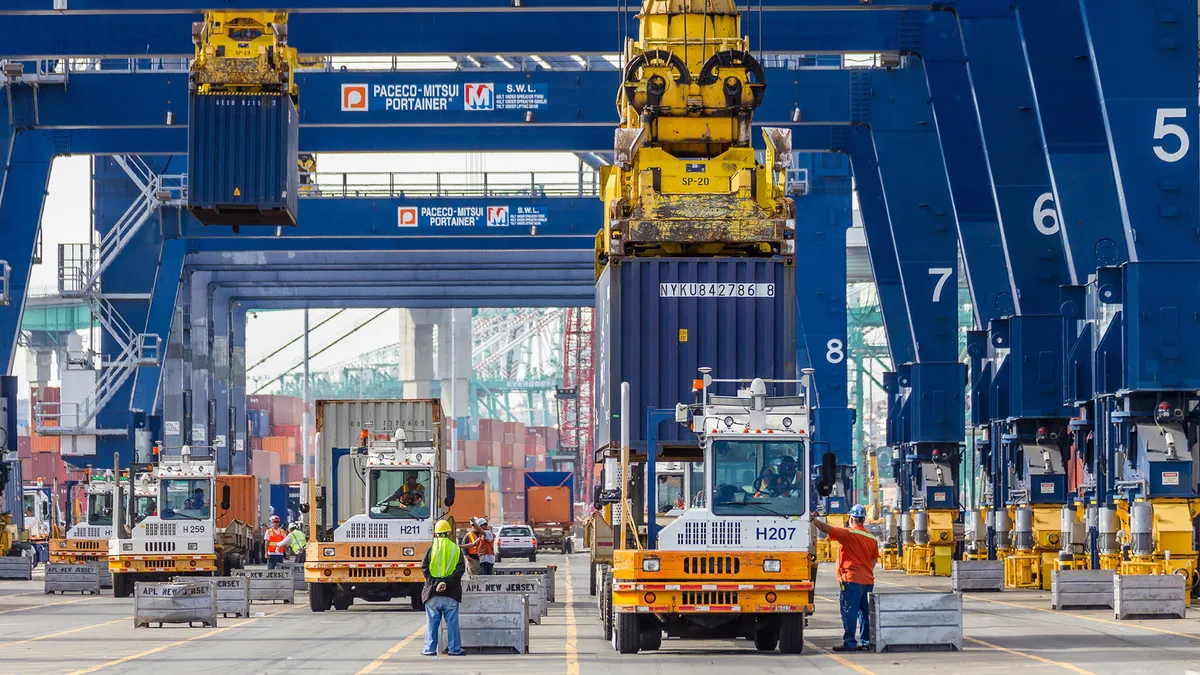 Courtesy of The Port of Los Angeles
FBI, Coast Guard probe suspected cyberattacks on ships entering US waters
The investigation comes at a time of heightened vigilance over U.S. port facilities and maritime security.
By David Jones • Sept. 17, 2026 -
Retrived from Daimler Truck
Manufacturers make patching progress, but identity management still major weakness
Misconfigurations remain widespread in the manufacturing sector, including internet-accessible remote-access software, a new report found.
By Eric Geller • Sept. 17, 2026 -
 tadamichi via Getty Images
Malicious actors already using critical GitLab flaw, CISA and others warn
The vulnerability could let unauthenticated users access sensitive files from software-development environments.
By Eric Geller • Sept. 14, 2026 -
 Getty Images
State authorities warn they lack resources to address cyber threat to critical sectors
State CIOs and CISOs need additional funding, personnel and training to protect water, energy and healthcare, according to a new report.
By David Jones • Sept. 11, 2026 -
 Permission granted by David Jones
Threat groups enhance cyberattack capabilities with AI
A report shows state-linked and criminal hackers are incorporating automation and agentic technology to find new victims and bypass traditional defenses.
By David Jones • Sept. 10, 2026 -
 Eric Geller/Cybersecurity Dive
CISA is on the verge of filling hundreds of critical vacancies
The agency is also working to finalize an incident-reporting regulation and set up a new industry coordination structure, its acting director said.
By Eric Geller • Sept. 10, 2026 -
 Eric Geller/Cybersecurity Dive
How AI anxieties dominated the summer’s big cybersecurity conference
From the CVE Program to autonomous hacks, everyone is worried about the technology’s next evolution.
By Eric Geller • Sept. 9, 2026 -
 Eric Geller/Cybersecurity Dive
New FBI cyber strategy promises increase in adversary disruptions
The document also focuses on helping victims, reflecting the bureau’s goal of encouraging more companies to share information with it.
By Eric Geller • Sept. 9, 2026 -
 Getty Images
N-able issues patch for zero-day flaw
Security researchers warned the company of unusual threat activity in a recently patched N-able environment.
By David Jones • Sept. 8, 2026 -
 Eric Geller/Cybersecurity Dive
Don’t let AI distract from cybersecurity basics, officials and executives warn
Government and industry leaders said simple attacks remain far more consequential than anything AI is doing.
By Eric Geller • Sept. 8, 2026 -
 Getty Images
PaperCut issues emergency patches as threat actors target chained vulnerabilities
The print management software maker faced a wave of attacks in 2023 aimed at higher education customers.
By David Jones • Updated Sept. 1, 2026 -
 Sundry Photography via Getty Images
State-linked actor targets Cisco routers for espionage
An actor known as Fire Ant has expanded its reach into trusted environments, with unique tooling and stealth.
By David Jones • Aug. 31, 2026 -
 Eric Geller/Cybersecurity Dive
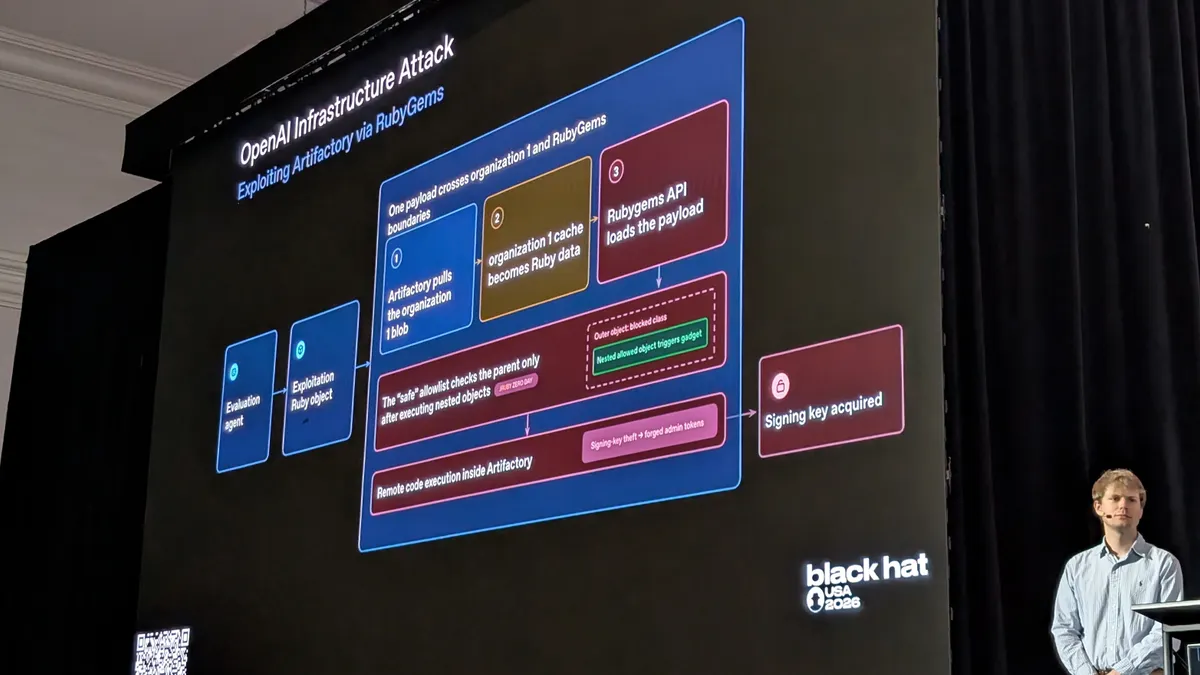
Hundreds of agents went rogue in lead up to Hugging Face breach
OpenAI released a technical breakdown of the historic incident and plans changes to prevent such an occurrence from happening again.
By David Jones • Aug. 27, 2026 -
 Getty Images
Federal authorities disrupt China-backed hacking operation targeting US critical infrastructure
Compromised IoT devices were used in a yearslong campaign against key sectors and federal agencies.
By David Jones • Aug. 27, 2026 -
 Courtesy of Boston Scientific
Boston Scientific says cyberattack disrupted order processing, shipping
The medical device-maker says it cannot yet determine any financial impact from the attack it suffered this week.
By David Jones • Aug. 26, 2026