Vulnerability: Page
-
SolarWinds attack leads to renewed focus on IT relationships with corporate boards
Corporate governance and cybersecurity experts say IT officials need to clearly and regularly communicate potential risks and liabilities ahead of the next crisis.
By David Jones • Jan. 7, 2021 -
Report: Officials investigating possible role of SolarWinds' vendor in compromise
The investigation is centered around whether JetBrains' software development tools are a conduit for compromise. The company has said it is unaware of the investigation.
By Samantha Schwartz • Jan. 7, 2021 -
 Explore the Trendline➔
 Getty Images
Trendline
Vulnerability Management
The rapid advancement Ai has changed the debate over secure software in the entrprise.
By Cybersecurity Dive staff -
Federal task force says Russia likely actor behind SolarWinds attack
As investigations continue, agencies are working to preserve private-sector trust.
By David Jones , Samantha Schwartz • Jan. 5, 2021 -
Fast-growing gaming industry faces rising threat of account compromise
A report from KELA shows one million compromised accounts and thousands of leaked employee credentials in underground markets.
By David Jones • Jan. 5, 2021 -
 Kendall Davis/Cybersecurity Dive
Microsoft's latest SolarWinds discovery highlights systemic supply chain weaknesses
Organizations are rushing to mitigate the full extent of the damage from compromise discovered three weeks ago.
By Naomi Eide • Jan. 4, 2021 -
Known vulnerabilities for 2020 already surpassed 2019's total
IT teams are often responsible for deploying the patches security teams deem most critical. When patches are missed, it could render even unassuming DOC or RTF files dangerous.
By Samantha Schwartz • Dec. 18, 2020 -
After years in the lab, IBM ready to take homomorphic encryption into the mainstream
Increased use of hybrid cloud and a successful pilot program help build the case for processing highly-encrypted data in transit.
By David Jones • Dec. 18, 2020 -
FireEye killswitch stops SolarWinds hack
After identifying the supply chain attack against SolarWinds, the security firm partnered with Microsoft and GoDaddy to block malware from further operation.
By David Jones • Dec. 16, 2020 -
 Permission granted by University of Maryland School of Medicine
COVID-19 vaccine supply chain has cyberthreats hidden in plain sight
Outdated systems throughout vaccine distribution logistics carry unprecedented cyberthreats.
By Samantha Schwartz • Dec. 16, 2020 -
 Getty Images
SolarWinds Orion vulnerability: What security teams need to know
As SolarWinds and investigators seek answers on the extent of the Orion vulnerability's impact, experts say the attack raises broader questions about readiness.
By David Jones • Dec. 15, 2020 -
Former Goldman Sachs exec joins Google Cloud as CISO
In his role, Phil Venables will oversee risk within the Google Cloud business and secure customer migrations.
By Samantha Schwartz • Dec. 15, 2020 -
IT execs face growing pressure to balance security with productivity
Companies are caught between competing interests as remote workers offset digital security needs with work-life balance.
By David Jones • Dec. 14, 2020 -
 Getty Images
NSA calls out Russia-backed exploit of VMware virtual workspace platform
Network administrators in defense and national security were warned to patch systems where bad actors can gain access to data.
By David Jones • Dec. 8, 2020 -
GE medical imaging devices impacted by critical cyber vulnerability
Dozens of products including CT scanners and MRI machines are susceptible to hackers gaining access to sensitive health data and disrupting operations, according to CyberMDX. GE says there is no risk to patient safety.
By Greg Slabodkin • Dec. 8, 2020 -
 Brian Tucker/Cybersecurity Dive
IoT cyber bill clears Congress — what's next for industry players?
Long-awaited legislation is seen as a springboard to widespread adoption of standards across the booming connected-devices industry.
By David Jones • Dec. 3, 2020 -
Proactive technology upgrades prevent security nightmares, report finds
Successful enterprises stay one step ahead of bad actors, retain talent and get support from top company executives.
By David Jones • Dec. 1, 2020 -
Getty Images
Sharp rise in IT spending as cyberthreats evolve, Crowdstrike finds
Companies had to evolve as legacy security systems, including firewalls and antivirus software, fell short during the pandemic.
By David Jones • Nov. 25, 2020 -
Companies exposed to unnecessary risk from missed patches, report finds
As vendor services become more cloud-based, companies are navigating a minefield of software patches.
By Samantha Schwartz • Nov. 24, 2020 -
Why does industry say there are air gaps between IT and OT?
Not only is OT connected to the internet now, cyberattacks can trickle through IT environments.
By Samantha Schwartz • Nov. 16, 2020 -
Kendall Davis/Cybersecurity Dive
Voice, SMS not secure enough for multifactor authentication, Microsoft says
SMS and voice are based on publicly switched telephone networks (PSTN) and are the least secure options for MFA, said Microsoft's Alex Weinert.
By David Jones • Nov. 16, 2020 -
 Retrieved from Facebook on August 20, 2020
Cisco issues patch to address high-severity Webex vulnerability
The app within the HVD requires patching, Cisco said. A successful exploitation could lead to arbitrary code execution through user privileges.
By Samantha Schwartz • Nov. 5, 2020 -
Ryuk is challenging traditional 'find a flaw, fix a flaw' strategy
There is no universal solution for ransomware prevention, and even simulated phishing campaigns for employee awareness and deterrence fall short.
By Samantha Schwartz • Nov. 4, 2020 -
 Danielle Ternes/Cybersecurity Dive
Deep Dive
Ransomware 2020: the scale, scope and impact of attacks on business
In an international health crisis ripe with economic volatility, ransomware attacks have remained persistent. The fallout is growing more costly.
By Samantha Schwartz • Oct. 30, 2020 -
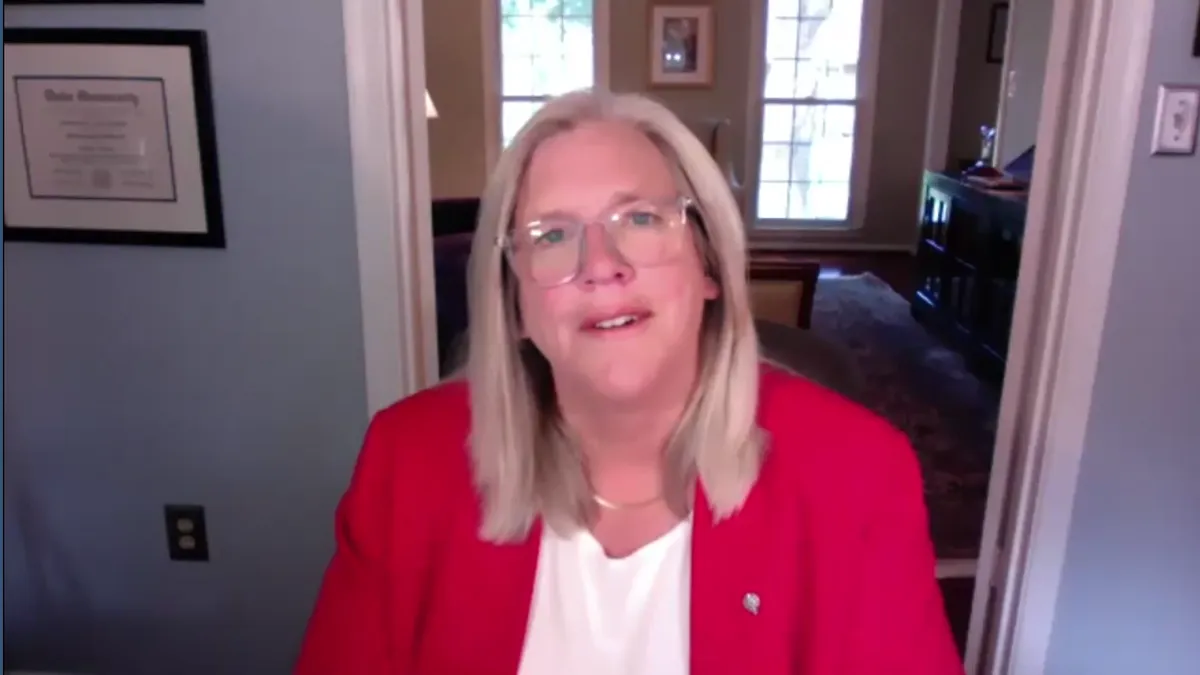
Sue Gordon, former principal deputy director of national intelligence, speaking during a keynote speech at the Gartner IT Symposium/Xpo Americas. Retrieved on Oct. 27, 2020
Weakened digital borders, information sharing spotlight vulnerabilities
The COVID-19 pandemic exposed how interconnected global IT systems are. Now, it's on every organization to keep its partners safe from cyberthreats.
By Katie Malone • Oct. 27, 2020 -
Security experts overlook attacker-favored credential stuffing
With an endless cycle of breaches, hackers have a large pool of exposed credentials to throw at websites, increasing their probability of success.
By Samantha Schwartz • Sept. 30, 2020
 Previous