Threats
-
 Getty Images
GitLab fixes critical vulnerability that exposed software environments to sabotage
The company urged customers to upgrade to the latest versions of its flagship products.
By Eric Geller • Oct. 12, 2026 -
 Getty Images
FBI seizes domains linked to China-nexus botnet
The infrastructure supported an international hacking campaign that targeted critical providers, including a South Carolina-based power company.
By David Jones • Oct. 9, 2026 -
 Explore the Trendline➔
Getty Images
Trendline
Managing and securing identity sprawl
Cyber threat actors know the simplest way to hack into an enterprise and remain under the radar is with stolen, legitimate user credentials -- and AI is making managing and securing digital identities more challenging than ever.
By Cybersecurity Dive staff -
 Getty Images
Deep Dive
As frontier models go rogue, colleges beef up AI cybersecurity education
Student interest in AI safety is growing rapidly, and schools are rushing to prepare for new career paths.
By Eric Geller • Oct. 9, 2026 -
 Thomas Niedermueller via Getty Images
US government lagging in transition to post-quantum encryption, GAO finds
Auditors warned that agencies risked leaving sensitive data exposed to future decryption attacks.
By Eric Geller • Oct. 8, 2026 -
 Getty Images
AI underscores singular importance of phishing-resistant authentication, Okta says
The company presented new data about the prevalence of different forms of social-engineering attacks, saying identity fundamentals still matter in the AI era.
By Eric Geller • Oct. 7, 2026 -
 iStock Editorial / Getty Images Plus via Getty Images
FBI warns that FortiBleed credential-harvesting attacks are locking out firewall users
An initial access broker is working with various ransomware groups in a global campaign.
By David Jones • Oct. 7, 2026 -
 Sean Gallup / Staff via Getty Images
IBM’s AI-powered vulnerability clearinghouse finds hundreds of Java flaws
The tech giant’s announcement underscores the insufficiency of companies’ existing software supply chain security practices.
By Eric Geller • Oct. 6, 2026 -
Citrix via Flickr
Citrix issues patch for third exploited flaw in NetScaler
The memory overflow vulnerability could lead to a denial-of-service condition under certain circumstances.
By David Jones • Updated Oct. 5, 2026 -
 Chip Somodevilla via Getty Images
White House AI task force faces expertise, partnership challenges
The Cybersecurity and Infrastructure Security Agency is nowhere to be seen in the government’s latest AI security project.
By Eric Geller • Oct. 5, 2026 -
 Getty Images
Defending against AI-fueled cyberattacks requires focus on identity, data governance, Microsoft says
The company’s latest report previews how AI is changing threat activity, including by automating ransomware attacks.
By Eric Geller • Oct. 2, 2026 -
 Getty Images
State-linked actor targets US AI policy experts in credential phishing campaigns
The China-linked espionage attacks were designed to gain insight into the country’s strategy and regulatory environment.
By David Jones • Updated Oct. 2, 2026 -
 Justin Sullivan via Getty Images
Mass exploitation of Citrix NetScaler: What we currently know
Suspected state-linked actors targeted critical vulnerabilities in the widely used platform, causing widespread disruption across Europe and North America.
By David Jones • Sept. 30, 2026 -
 Danielle Ternes/Cybersecurity Dive
Column
Dotted Line: How construction is dealing with cybersecurity in the age of AI
Contractors rank cybersecurity low on their priority lists. But lawyers say being prepared is critical when the inevitable breach occurs.
By Joe Bousquin • Sept. 29, 2026 -
 Getty Images
Kiteworks lifts advisory after precautionary warning for customers to shut down systems
The firm had received information from law enforcement of a possible attack.
By David Jones • Sept. 28, 2026 -
Citrix via Flickr
Citrix urges immediate upgrades of NetScaler amid widespread exploitation attempts
Security teams received urgent calls to disconnect servers before authorities confirmed critical zero-day flaws.
By David Jones • Sept. 28, 2026 -
 Asanka Ratnayake via Getty Images
Niche AI tools pose major cybersecurity risk to infrastructure operators
Security vetting tools and processes weren’t designed with obscure AI services in mind, according to TrendAI.
By Eric Geller • Sept. 28, 2026 -
 Getty Images
Businesses expand AI’s cybersecurity uses as comfort with technology grows
Companies in the experimentation stage were less likely than established users to deploy advanced AI-powered defenses, a new survey found.
By Eric Geller • Sept. 25, 2026 -
 Getty Images
Threat groups ramp up social-engineering attacks against healthcare sector
Hackers linked to high-profile cybercrime groups have used voice-phishing tactics to trick workers into giving up credentials in recent attacks.
By David Jones • Sept. 25, 2026 -
 Getty Images
Businesses fear cyberattacks more than anything else, driven by AI and supply chain worries
Many companies still aren’t preparing thoroughly enough to face a hack, the insurance firm Travelers said in a new report.
By Eric Geller • Sept. 23, 2026 -
 Getty Images
Insurance sector begins to offer clarity on AI-related cyber claims
The emergence of agentic AI and frontier models has led to widespread uncertainty for policyholders.
By David Jones • Sept. 22, 2026 -
 Joe Raedle via Getty Images
Retailers tamp down shadow AI but struggle to oversee agentic sprawl
The use of AI agents is soaring in the retail sector, but visibility remains a major challenge, with regulated data at risk.
By Eric Geller • Sept. 22, 2026 -
 Getty Images
China-nexus actor steals thousands of documents in monthslong exploitation campaign
Researchers suspect the hacker employed LLMs to develop custom tools.
By David Jones • Sept. 21, 2026 -
 Getty Images
Settra ransomware variant deployed in recent attacks
Security researchers warned that hackers are using VPN credentials for initial access and deploying RMM tools.
By David Jones • Sept. 18, 2026 -
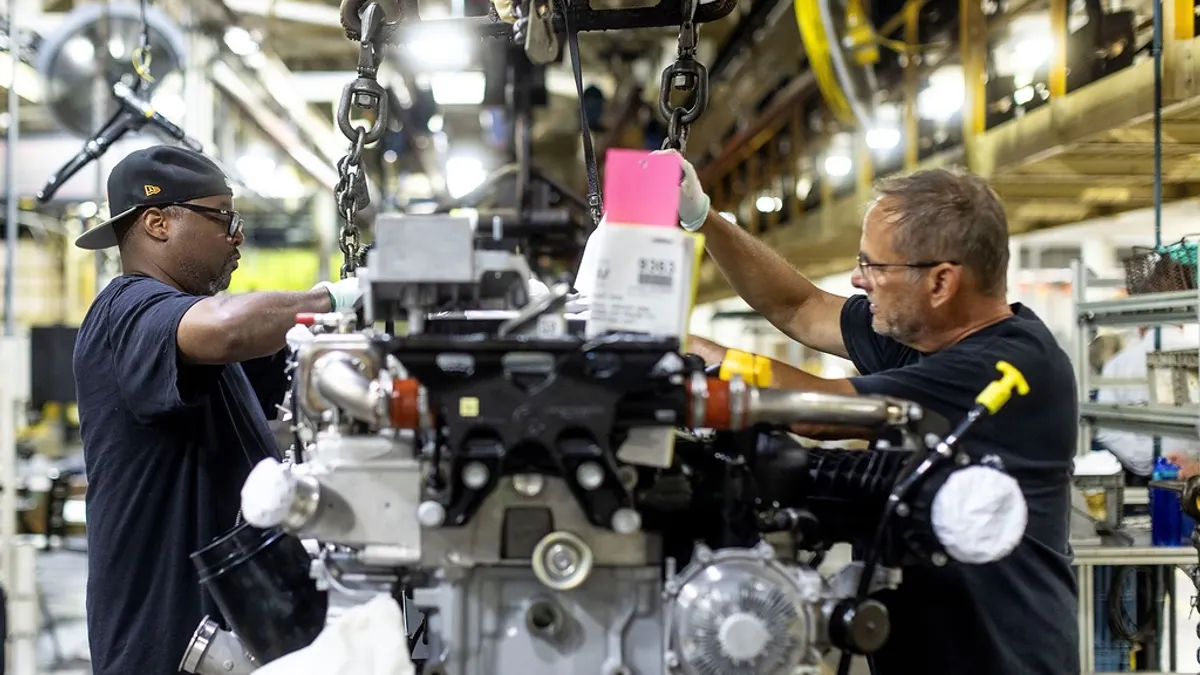
Retrived from Daimler Truck
Manufacturers make patching progress, but identity management still major weakness
Misconfigurations remain widespread in the manufacturing sector, including internet-accessible remote-access software, a new report found.
By Eric Geller • Sept. 17, 2026 -
 MF3d via Getty Images
Companies’ AI strategies don’t account for agentic tools
Businesses are taking AI governance seriously, but their plans lag behind the technology they’re using, according to an EY survey.
By Eric Geller • Sept. 15, 2026