Threats
-
 Getty Images
Settra ransomware variant deployed in recent attacks
Security researchers warned that hackers are using VPN credentials for initial access and deploying RMM tools.
By David Jones • Sept. 18, 2026 -
Retrived from Daimler Truck
Manufacturers make patching progress, but identity management still major weakness
Misconfigurations remain widespread in the manufacturing sector, including internet-accessible remote-access software, a new report found.
By Eric Geller • Sept. 17, 2026 -
 Explore the Trendline➔
Getty Images
Trendline
Securing against ransomware
Security professionals hail cybersecurity basics as the best defense against ransomware — regular patching, multifactor authentication and, maybe most importantly, information sharing.
By Cybersecurity Dive staff -
 MF3d via Getty Images
Companies’ AI strategies don’t account for agentic tools
Businesses are taking AI governance seriously, but their plans lag behind the technology they’re using, according to an EY survey.
By Eric Geller • Sept. 15, 2026 -
 tadamichi via Getty Images
Malicious actors already using critical GitLab flaw, CISA and others warn
The vulnerability could let unauthenticated users access sensitive files from software-development environments.
By Eric Geller • Sept. 14, 2026 -
 Permission granted by Arctic Wolf
Sponsored by Arctic Wolf
Security teams are adopting AI faster than they trust it
New survey data reveals a widening gap between AI adoption and AI trust.
Sept. 14, 2026 -
 Getty Images
Deep Dive
Accountability, oversight and AI: Inside Microsoft’s security transformation
Stung by years of embarrassing hacks, the tech giant overhauled how it approached cybersecurity. Company leaders now say they’re seeing results.
By Eric Geller • Sept. 11, 2026 -
 Permission granted by David Jones
Threat groups enhance cyberattack capabilities with AI
A report shows state-linked and criminal hackers are incorporating automation and agentic technology to find new victims and bypass traditional defenses.
By David Jones • Sept. 10, 2026 -
 Eric Geller/Cybersecurity Dive
White House sees water cybersecurity partnership in Texas as national blueprint
The government is taking a new approach to protecting critical infrastructure, National Cyber Director Sean Cairncross said.
By Eric Geller • Sept. 10, 2026 -
 Eric Geller/Cybersecurity Dive
CISA is on the verge of filling hundreds of critical vacancies
The agency is also working to finalize an incident-reporting regulation and set up a new industry coordination structure, its acting director said.
By Eric Geller • Sept. 10, 2026 -
 Eric Geller/Cybersecurity Dive
How AI anxieties dominated the summer’s big cybersecurity conference
From the CVE Program to autonomous hacks, everyone is worried about the technology’s next evolution.
By Eric Geller • Sept. 9, 2026 -
 Sean Gallup via Getty Images
CISOs are feeling the security burden of accelerated AI use
A report shows CISOs face increased pressures related to cyber resilience and business continuity.
By David Jones • Sept. 9, 2026 -
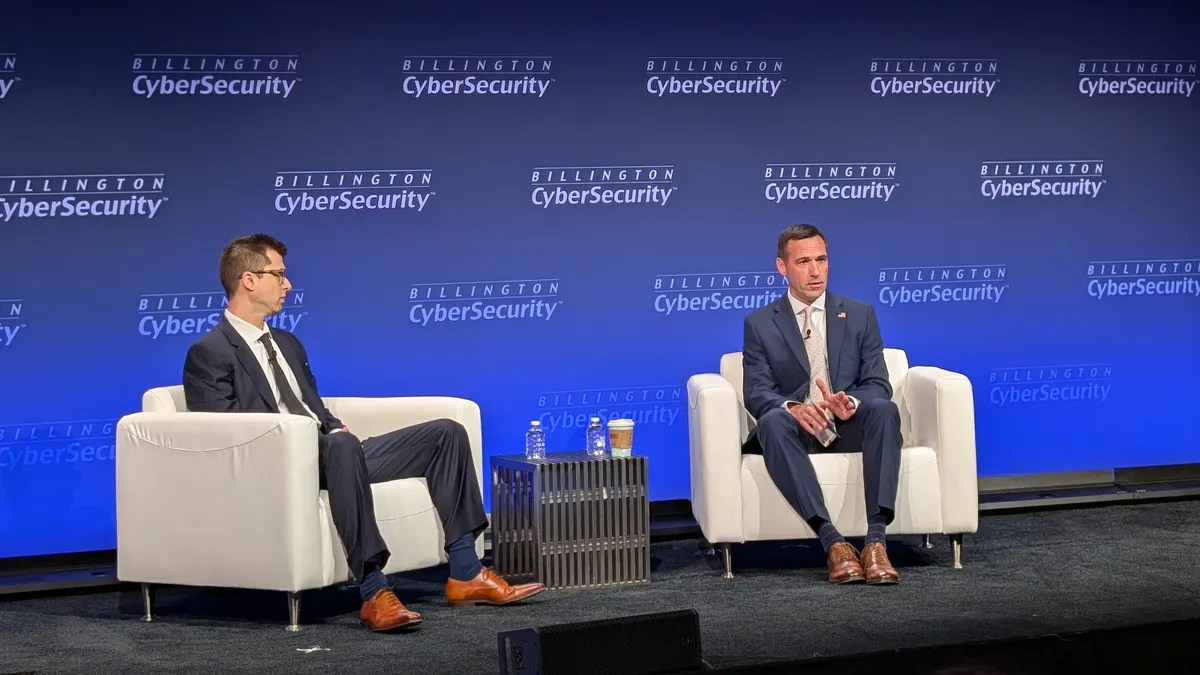 Eric Geller/Cybersecurity Dive
New FBI cyber strategy promises increase in adversary disruptions
The document also focuses on helping victims, reflecting the bureau’s goal of encouraging more companies to share information with it.
By Eric Geller • Sept. 9, 2026 -
 Eric Geller/Cybersecurity Dive
Don’t let AI distract from cybersecurity basics, officials and executives warn
Government and industry leaders said simple attacks remain far more consequential than anything AI is doing.
By Eric Geller • Sept. 8, 2026 -
 Getty Images
Sponsored by Okta
Essential AI agent security questions
AI agents are outpacing legacy IAM. Discover the 3 questions every CISO must ask to secure them.
By Patrick Schmitt Manager, Product Marketing Management, Analyst Relations • Sept. 8, 2026 -
 Getty Images
OpenAI pledges $1B to provide resources, training for frontline cyber defenders
Amid heightened scrutiny, the company will use frontier AI to help water, power and local government providers fight malicious actors.
By David Jones • Sept. 4, 2026 -
 Andrew Harnik via Getty Images
Government, industry partner to shut down long-running Sality botnet
A nonprofit group is now working to contact victims.
By Eric Geller • Sept. 3, 2026 -
 Getty Images
Government lacks ability to verify AI labs’ claims, experts say
A new survey of national security practitioners identified a wide range of near- and medium-term AI risks for policymakers to consider.
By Eric Geller • Sept. 3, 2026 -
 Courtesy of Office of the Texas Governor
Frontier AI helps exploit flaws in tests using key industrial devices
A report showed that Claude could help hackers develop attack strategies targeting PLCs used by water utilities and other industries.
By David Jones • Sept. 1, 2026 -
 Sundry Photography via Getty Images
State-linked actor targets Cisco routers for espionage
An actor known as Fire Ant has expanded its reach into trusted environments, with unique tooling and stealth.
By David Jones • Aug. 31, 2026 -
 Matt Kapko/Cybersecurity Dive
Frontier AI tipping the scales toward cyber adversaries
Researchers at Palo Alto Networks’ Unit 42 warn that threat actors are already using AI to accelerate cyberattacks beyond the abilities of modern defenses.
By David Jones • Aug. 28, 2026 -
 Eric Geller/Cybersecurity Dive
CISA identifies security hurdles that led to very different results in two red-team engagements
The agency said its recent simulated cyberattacks offered several key lessons for many organizations.
By Eric Geller • Aug. 28, 2026 -
 Getty Images
Federal authorities disrupt China-backed hacking operation targeting US critical infrastructure
Compromised IoT devices were used in a yearslong campaign against key sectors and federal agencies.
By David Jones • Aug. 27, 2026 -
 Chip Somodevilla via Getty Images
Treasury to help financial firms transition to quantum-resistant encryption
The government is concerned that hackers could someday decrypt financial information and other secrets using code-breaking quantum computers.
By Eric Geller • Aug. 26, 2026 -
 Getty Images
Researchers warn about chained SharePoint sequence
An authentication bypass flaw is already under exploitation, the latest in a series of recent SharePoint attacks.
By David Jones • Updated Aug. 26, 2026 -
tadamichi via Getty Images
CISA orders agencies to fix exploited Zimbra vulnerability
The collaboration software’s developer took almost a full month to patch the flaw after disclosing it.
By Eric Geller • Aug. 25, 2026