Policy & Regulation
-
 Getty Images
FBI seizes domains linked to China-nexus botnet
The infrastructure supported an international hacking campaign that targeted critical providers, including a South Carolina-based power company.
By David Jones • Oct. 9, 2026 -
 Getty Images
What the C-suite needs to know about AI governance
As AI adoption surges, executives are learning tough lessons about security, oversight and accountability.
By David Jones • Oct. 8, 2026 -
 Explore the Trendline➔
Getty Images
Trendline
AI
AI has boosted cyber threat actors, but it’s also given defenders new tools. Which side will prevail?
By Cybersecurity Dive staff -
 Thomas Niedermueller via Getty Images
US government lagging in transition to post-quantum encryption, GAO finds
Auditors warned that agencies risked leaving sensitive data exposed to future decryption attacks.
By Eric Geller • Oct. 8, 2026 -
 Tomohiro Ohsumi via Getty Images
US cyber resilience, oversight tested in series of attacks
Attacks targeting key industrial sites and unforced errors among leading AI companies are raising alarm bells.
By David Jones • Oct. 6, 2026 -
 Chip Somodevilla via Getty Images
White House AI task force faces expertise, partnership challenges
The Cybersecurity and Infrastructure Security Agency is nowhere to be seen in the government’s latest AI security project.
By Eric Geller • Oct. 5, 2026 -
 ATHVisions via Getty Images
Sponsored by ServiceNow
Why permissions must be the foundation for next-gen identity security
Authentication isn't enough. Monitor access across humans, machines and AI agents.
Oct. 5, 2026 -
 Getty Images
State-linked actor targets US AI policy experts in credential phishing campaigns
The China-linked espionage attacks were designed to gain insight into the country’s strategy and regulatory environment.
By David Jones • Updated Oct. 2, 2026 -
 Eric Geller/Cybersecurity Dive
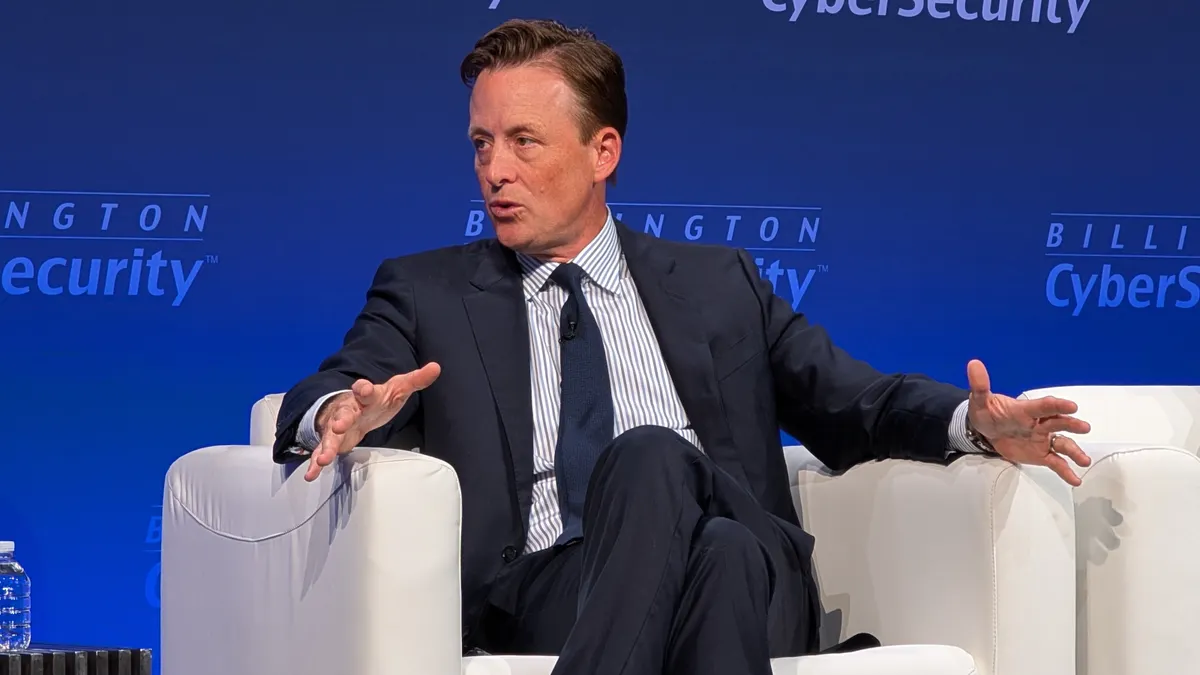
National cyber director defends private-sector hacking program, urges focus on security basics
Letting businesses help the government deter cybercrime will benefit all Americans, Sean Cairncross said.
By Eric Geller • Sept. 30, 2026 -
 Win McNamee via Getty Images
GAO report spotlights industry’s concerns about overlapping cybersecurity regulations
Representatives of three critical infrastructure sectors identified the conflicting and redundant rules that they said made their jobs more difficult.
By Eric Geller • Sept. 29, 2026 -
 ATHVisions via Getty Images
Sponsored by ServiceNow
Context matters when it comes to cybersecurity’s agentic operating model
AI agents need context-aware security beyond traditional models. Workflow data provides the governance guardrails that make AI safe and scalable.
Sept. 28, 2026 -
Tomohiro Ohsumi via Getty Images
Rogue OpenAI agent targeted Australian government site
The prime minister rebuked the company for its slow response and warned that AI poses significant risks that need to be further addressed.
By David Jones • Sept. 24, 2026 -
 Eric Geller/Cybersecurity Dive
CISA is on the verge of filling hundreds of critical vacancies
The agency is also working to finalize an incident-reporting regulation and set up a new industry coordination structure, its acting director said.
By Eric Geller • Sept. 10, 2026 -
 Getty Images
Government lacks ability to verify AI labs’ claims, experts say
A new survey of national security practitioners identified a wide range of near- and medium-term AI risks for policymakers to consider.
By Eric Geller • Sept. 3, 2026 -
 Eric Geller/Cybersecurity Dive
CISA scraps 6 free cybersecurity assessments for critical infrastructure operators
The agency’s decision, spurred by workload concerns, could leave organizations without valuable insights into their vulnerabilities.
By Eric Geller • Updated Sept. 3, 2026 -
 Getty Images
Federal authorities disrupt China-backed hacking operation targeting US critical infrastructure
Compromised IoT devices were used in a yearslong campaign against key sectors and federal agencies.
By David Jones • Aug. 27, 2026 -
 Chip Somodevilla via Getty Images
Treasury to help financial firms transition to quantum-resistant encryption
The government is concerned that hackers could someday decrypt financial information and other secrets using code-breaking quantum computers.
By Eric Geller • Aug. 26, 2026 -
 Courtesy of National Cyber Security Centre
UK power facility disabled for days after suspected state-linked cyberattack
The disruption took place amid a wave of attacks targeting vulnerable industrial devices in the water and energy sectors.
By David Jones • Aug. 24, 2026 -
 Getty Images
House Democrats ask GAO to study CISA workforce cuts
Five lawmakers serving on the Homeland Security Committee said Congress didn’t know enough about the Trump administration’s changes to the cybersecurity agency.
By Eric Geller • Aug. 24, 2026 -
 Getty Images
Defense contractors still struggling with basic CMMC requirements
A “confidence disconnect” is plaguing the industry, a consulting firm said.
By Eric Geller • Aug. 21, 2026 -
 Getty Images
What we know so far about the hacking campaign against US water systems
Support is growing for stricter oversight and increased financial resources for utilities in the wake of a cyberattack spree, suspected to be the work of Iran-linked threat groups.
By David Jones • Aug. 20, 2026 -
 Getty Images
AI-backed campaign targeting vulnerable Siemens S7 devices, CISA and FBI warn
Hackers are developing scripts disguised as legitimate software in attacks aimed at multiple industries, including energy and water.
By David Jones • Updated Aug. 20, 2026 -
 Getty Images
DOJ charges 17 people in Iran-backed hacking campaign against US
Officials allege an IRGC-linked organization was behind a coordinated effort to steal research from American universities, companies and government agencies.
By David Jones • Updated Aug. 19, 2026 -
Chip Somodevilla via Getty Images
Deep Dive
AI-powered vulnerability clearinghouse faces deep skepticism, major challenges
The U.S. government’s promises about the Gold Eagle coordination program are overblown, experts said, but the initiative could help organizations prioritize patching and mitigation.
By Eric Geller • Aug. 18, 2026 -
 Getty Images
Deep Dive
CVE Program eyes automation and globalization to weather AI ‘vulnpocalypse’
The vulnerability coordination project has had a rocky few years, but a key leader says it will “flourish and improve.”
By Eric Geller • Aug. 11, 2026 -
 Getty Images
Experts say healthcare faces cybersecurity crisis: ‘These are patient safety issues’
Regulatory failures, funding constraints and industry consolidation have created serious hacking risks.
By Eric Geller • Aug. 7, 2026