Leadership & Careers
-
 Eric Geller/Cybersecurity Dive
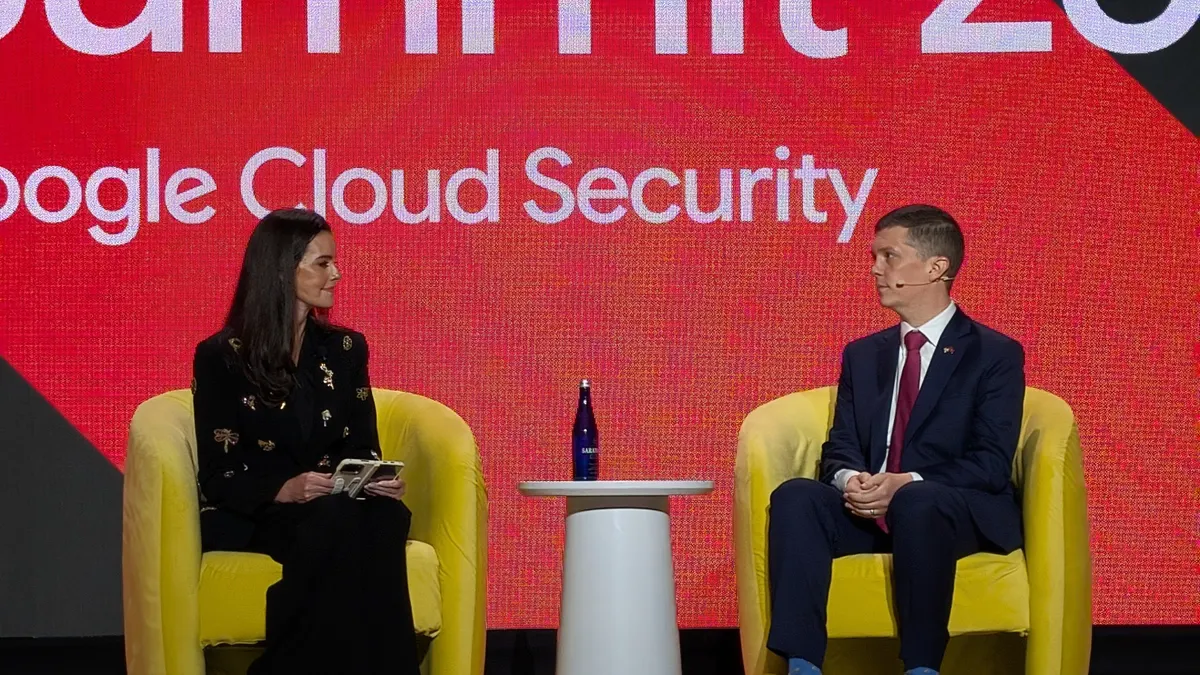
CISA looks to recruit general infrastructure security experts rather than sector-focused advisers
“I need people that can pivot from day to day,” the agency’s acting chief told reporters.
By Eric Geller • Sept. 16, 2026 -
 MF3d via Getty Images
Companies’ AI strategies don’t account for agentic tools
Businesses are taking AI governance seriously, but their plans lag behind the technology they’re using, according to an EY survey.
By Eric Geller • Sept. 15, 2026 -
 Explore the Trendline➔
Getty Images
Trendline
CISO Strategy
AI is rapidly transforming the cybersecurity landscape, and CISOs must keep pace.
By Cybersecurity Dive staff -
 Getty Images
Deep Dive
Accountability, oversight and AI: Inside Microsoft’s security transformation
Stung by years of embarrassing hacks, the tech giant overhauled how it approached cybersecurity. Company leaders now say they’re seeing results.
By Eric Geller • Sept. 11, 2026 -
 Eric Geller/Cybersecurity Dive
White House sees water cybersecurity partnership in Texas as national blueprint
The government is taking a new approach to protecting critical infrastructure, National Cyber Director Sean Cairncross said.
By Eric Geller • Sept. 10, 2026 -
 Eric Geller/Cybersecurity Dive
CISA is on the verge of filling hundreds of critical vacancies
The agency is also working to finalize an incident-reporting regulation and set up a new industry coordination structure, its acting director said.
By Eric Geller • Sept. 10, 2026 -
 Eric Geller/Cybersecurity Dive
How AI anxieties dominated the summer’s big cybersecurity conference
From the CVE Program to autonomous hacks, everyone is worried about the technology’s next evolution.
By Eric Geller • Sept. 9, 2026 -
 Sean Gallup via Getty Images
CISOs are feeling the security burden of accelerated AI use
A report shows CISOs face increased pressures related to cyber resilience and business continuity.
By David Jones • Sept. 9, 2026 -
 Eric Geller/Cybersecurity Dive
New FBI cyber strategy promises increase in adversary disruptions
The document also focuses on helping victims, reflecting the bureau’s goal of encouraging more companies to share information with it.
By Eric Geller • Sept. 9, 2026 -
 Eric Geller/Cybersecurity Dive
Don’t let AI distract from cybersecurity basics, officials and executives warn
Government and industry leaders said simple attacks remain far more consequential than anything AI is doing.
By Eric Geller • Sept. 8, 2026 -
 Justin Sullivan / Staff via Getty Images
Nvidia’s $12.9B Hugging Face deal could benefit enterprises
The chipmaker’s acquisition could eventually bring additional security resources and model evaluation tools to the platform, according to experts.
By Paige Gross • Sept. 4, 2026 -
 Andrew Harnik via Getty Images
Government, industry partner to shut down long-running Sality botnet
A nonprofit group is now working to contact victims.
By Eric Geller • Sept. 3, 2026 -
 Getty Images
Government lacks ability to verify AI labs’ claims, experts say
A new survey of national security practitioners identified a wide range of near- and medium-term AI risks for policymakers to consider.
By Eric Geller • Sept. 3, 2026 -
 Eric Geller/Cybersecurity Dive
CISA scraps 6 free cybersecurity assessments for critical infrastructure operators
The agency’s decision, spurred by workload concerns, could leave organizations without valuable insights into their vulnerabilities.
By Eric Geller • Updated Sept. 3, 2026 -
 Chip Somodevilla via Getty Images
Treasury to help financial firms transition to quantum-resistant encryption
The government is concerned that hackers could someday decrypt financial information and other secrets using code-breaking quantum computers.
By Eric Geller • Aug. 26, 2026 -
 Getty Images
House Democrats ask GAO to study CISA workforce cuts
Five lawmakers serving on the Homeland Security Committee said Congress didn’t know enough about the Trump administration’s changes to the cybersecurity agency.
By Eric Geller • Aug. 24, 2026 -
 Getty Images
Fitch explains how water, healthcare organizations can keep strong credit ratings despite cyberattacks
Resilience, not prevention, is key, analysts at the credit-rating agency said in a pair of new reports.
By Eric Geller • Aug. 20, 2026 -
 Chip Somodevilla via Getty Images
Deep Dive
AI-powered vulnerability clearinghouse faces deep skepticism, major challenges
The U.S. government’s promises about the Gold Eagle coordination program are overblown, experts said, but the initiative could help organizations prioritize patching and mitigation.
By Eric Geller • Aug. 18, 2026 -
 katleho Seisa via Getty Images
US government will let private companies hack criminal gangs
The new program, meant to aggressively disrupt costly cybercrime schemes, carries numerous legal and security risks.
By Eric Geller • Updated Aug. 13, 2026 -
 Getty Images
Deep Dive
CVE Program eyes automation and globalization to weather AI ‘vulnpocalypse’
The vulnerability coordination project has had a rocky few years, but a key leader says it will “flourish and improve.”
By Eric Geller • Aug. 11, 2026 -
 Eric Geller/Cybersecurity Dive
AI firms know policymakers won’t ‘let you make a Terminator factory,’ DHS official says
The Trump administration believes leading AI companies have learned important lessons from recent incidents and regulation isn’t necessary to preserve those lessons.
By Eric Geller • Aug. 7, 2026 -
 Eric Geller/Cybersecurity Dive
Western government leaders call for a focus on infrastructure resilience, not AI hype
U.S. and allied officials said companies should start preparing now for a cyberattack that changes how they provide essential services.
By Eric Geller • Aug. 5, 2026 -
 Courtesy of Billington
CISA is prioritizing work with critical infrastructure as it begins to recover from cuts
The agency has been focused on helping secure systems at drinking and wastewater utilities in recent weeks.
By David Jones • Aug. 5, 2026 -
 MF3d via Getty Images
Tech industry alliance proposes AI agent safety reporting program
The information-sharing exchange is designed to widely share lessons learned from agentic AI security incidents.
By Eric Geller • Aug. 4, 2026 -
 Heather Diehl via Getty Images
Shadow AI, leadership resistance make AI governance tough for worried CISOs
Fewer than half of CISOs think their bosses see AI security as a business enabler, according to an Okta survey.
By Eric Geller • July 30, 2026 -
 Getty Images
As data breaches grow costlier, ungoverned AI creates new risks
Meanwhile, many companies still aren’t doing the basics to protect on-premises data, IBM found.
By Eric Geller • July 29, 2026