

ADEX, the AI-driven anti-fraud and traffic-quality platform within AdTech Holding, has uncovered an advertising campaign that used a hacked Thai college website to redirect users to an online casino, without relying on a single line of cloaking code. The technique is not confined to any one region: security researchers have documented the same domain-borrowing tactic on trusted sites from Turkey to Vietnam.
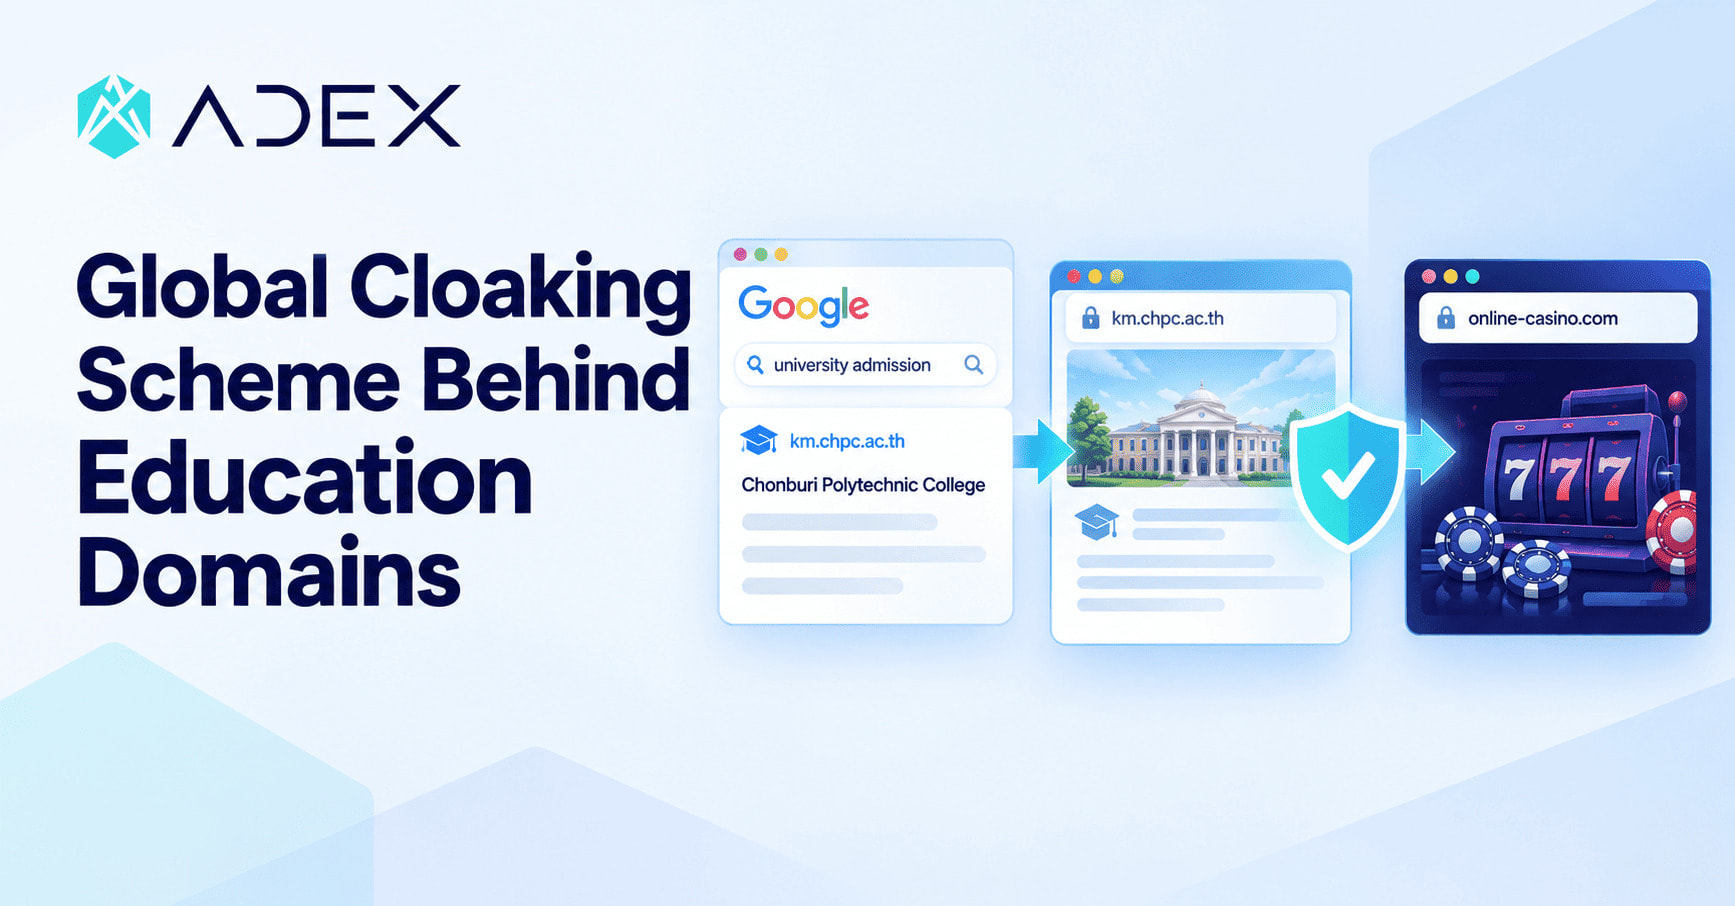
ADEX's monitoring team flagged an advertiser whose traffic was routed through what looked like an ordinary Google search, rather than a direct landing page. The top result on that search was km.chpc.ac.th, the genuine domain of a Thai college, sitting in the .ac.th zone reserved for educational institutions. Unknown to the college, the site had been hacked and a casino-themed page planted on it, which Google had indexed and ranked first for the query. A single click on that trusted result redirected the user to an online casino, a product illegal to advertise in Thailand.
What makes the case unusual, is that no part of the chain was fabricated. Classic cloaking runs on a fraudster's own server, detecting whether a visitor is a crawler or a person and serving different content accordingly. Here, every element, the Google search, the college website, and the redirect, was genuinely what it claimed to be. Only the combination created the violation: a moderator or crawler reviewing the ad's destination URL saw a neutral Google search page and nothing else, since the malicious step happened one click later, on a third-party site outside the campaign's own infrastructure.
A Global Pattern, Not a Regional One
Public data suggests the technique is widespread. Thailand's Ministry of Digital Economy and Society has reported roughly 30 million gambling-related URLs across about a thousand public-sector sites, with the Ministry of Public Health alone accounting for some 8 million injected scripts. Indonesia's Ministry of Communication and Informatics has blocked 683 government and educational sites injected with gambling content, 461 of them in the .go.id zone and 222 in .ac.id. An August 2025 academic study crawling Indonesian domains found 147 compromised sites and 346 pages carrying gambling keywords, with the academic .ac.id zone the hardest hit at 65 sites. The majority of that content is hidden from human visitors through CSS tricks, invisible to users but fully visible to search engine crawlers, the same underlying mechanic ADEX found on the Thai college site, executed through markup rather than a redirect.
The pattern shows up far outside Southeast Asia, too. Cybersecurity firm Netcraft has tracked an underground marketplace offering buyers access to more than 15,000 already-compromised .gov, .edu, and country-code domains for the same purpose, with campaigns concentrated on Turkey's gambling market. Separately, researchers at cSide identified an injection campaign hitting over 500 government and university websites globally, hiding gambling and adult-content links from human visitors while leaving them fully visible to search crawlers. Vietnam has flagged the identical dynamic on its own .gov.vn and .edu.vn domains, pointing to under-investment in cybersecurity at public institutions as the reason attackers keep returning to them.
The industry has started to respond. In March 2024, Google added a rule to its spam policies called site reputation abuse, targeting sites that publish someone else's content to borrow their ranking, and tightened it further in November 2024 to close the exception for site owners who claimed no involvement. The rule offers little protection in cases like this one, however: a hacked college was not a knowing participant, and the policy is written for sites that rent out their reputation deliberately, not ones victimized by it.
"One of the first things we tell ad networks and advertisers is to treat restricted domain zones, ac.*, .gov, .edu, .mi.*, .go.* as a flag rather than a pass whenever they turn up in a redirect chain, not an automatic block, since the campaign behind them may be entirely legitimate. Checking a single landing page is not enough, because in a case like this one, the landing page itself breaks no rule at all. Whatever is malicious sits behind it," explained ADEX.
What It Means For the Industry
According to ADEX, using compromised infrastructure for cloaking is not new, only more ambitious than before. "The domain as a trust signal stopped working long before this, back when malware started being distributed through the CDNs of major players," states the company. Attackers previously stuck to obscure or semi-abandoned domains; the shift is toward higher-profile, more trusted targets.
The conclusion for advertisers and networks, ADEX argues, is that a respectable domain appearing in a redirect chain should prompt closer scrutiny of where the click actually ends up, rather than serve as a reason to stop checking. ADEX recommends re-checking campaigns after approval, since a redirect chain can be rewired at any point, and treating a valid TLS certificate as no guarantee of legitimacy. For site owners, the firm points to two preventive habits: keeping an inventory of forgotten subdomains, which can quietly lend a site's reputation to whoever claims them, and periodically searching their own domain the way an attacker would, since injected pages are built to stay hidden from ordinary visitors.
ADEX is the AI-driven anti-fraud and traffic-quality platform within AdTech Holding. It analyzes billions of impressions, clicks, and conversions, protecting AdTech products and partners from malware-driven and invalid traffic attacks.