Months before hackers targeted refrigeration equipment across hundreds of grocery stores in France, a U.S.-based cybersecurity firm discovered high-severity flaws in internet-exposed equipment that could make such an attack possible.
Hackers reportedly were able to manipulate refrigeration systems in an attack beginning late Sunday, raising the temperature to 120 degrees Fahrenheit, leading to fires and spoiled food supplies.
Researchers at Claroty, in an August report, warned of multiple flaws in the web management interface of Danfoss AK-SM 800A controllers, which are used in refrigeration equipment across multiple industries.
Researchers demonstrated the ability of a malicious hacker to shut off cooling to a compromised controller, while staff using the equipment would still believe temperatures were normal.
Claroty disclosed the vulnerabilities to Danfoss, and the Danish manufacturer issued an advisory for two vulnerabilities, including CVE-2025-41451 and CVE-2025-41452.
The company issued a new firmware version for the vulnerabilities in 2025, and Claroty researchers discussed the findings at a presentation at DEF CON in Las Vegas in August.
ANSSI, the French national cybersecurity agency, released an updated advisory on Tuesday, warning the attacks also impacted Copeland xweb and Dixell xweb controllers. There is no specific information on any threat actor that may be behind the attacks.
HVAC leader
Danfoss is one of the largest manufacturers of refrigeration and HVAC systems in the world, and its systems are used in a wide variety of industries, including warehouses, cold-storage facilities, grocery chains and commercial buildings.
“Industrial control systems such as refrigeration controllers are often assumed to be on safely controlled networks, however our research found many of these devices are directly exposed to the internet,” Amir Preminger, CTO at Claroty, told Cybersecurity Dive.
Hundreds of supermarkets across multiple chains were directly impacted, including Carrefour, Monoprix and grocers owned by Cooperative U.
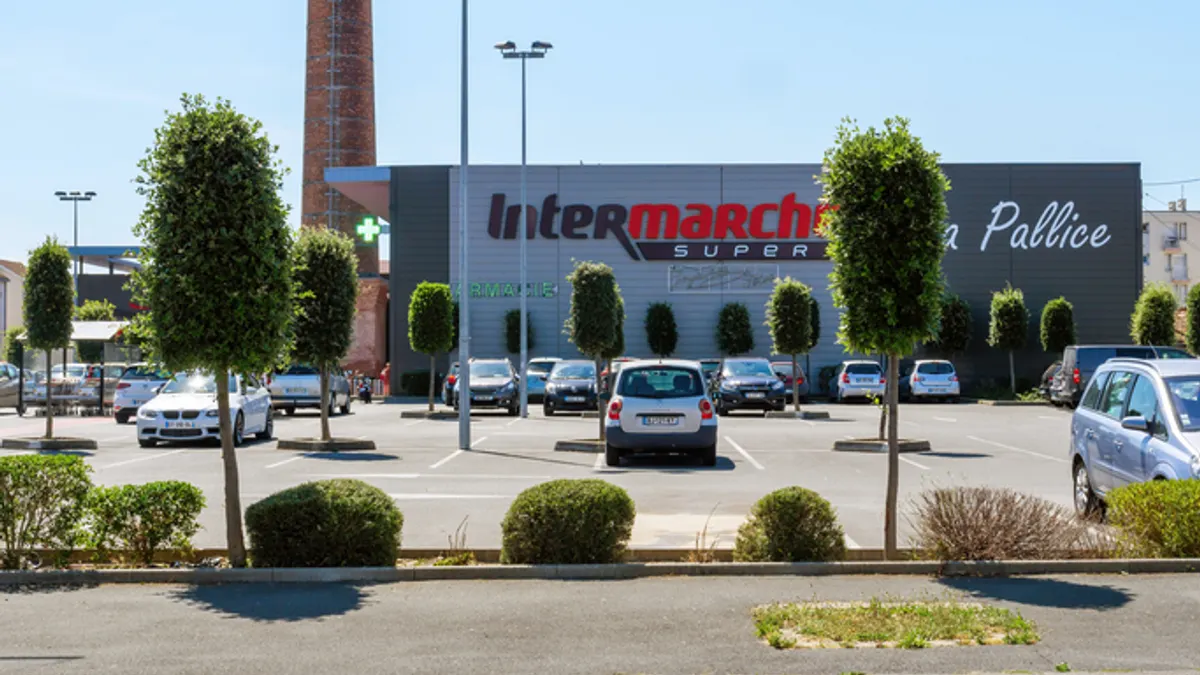
About 300 Intermarché and Netto stores were affected by the attack, which reportedly targeted a service provider that manages refrigeration equipment at the stores.
“Intermarché and Netto have taken all necessary precautions to remove the products from these units as quickly as possible,” a spokesperson for Groupement Mousquetaire, told Cybersecurity Dive.
Security teams should remove the vulnerable systems from the internet and restore access only behind a secure VPN or protected network, according to the advisory.
Danfoss representatives were not immediately available for comment.